O'Prueba Logo
News
OrpheLinkOrpheAgentRelease NotesDownload
Use CasesBlogManual
繁體中文 English
News
OrpheLinkOrpheAgentRelease NotesDownload
Use Cases Blog Manual
中文 EN
OrpheLink

Centrally Manage Who Can Connect — and What They Can Reach

OrpheLink is the control plane for enterprise remote access, centralizing identities, devices, access policies, ACLs, and network topology.

Together with OrpheAgent, it enables controlled Zero Exposure connectivity without public IPs, VPN gateways, or open ports.

Deploy in the cloud, hybrid environments, or fully on-prem while retaining control over architecture and data.

Start for Free

OrpheLink Manages Connectivity. OrpheAgent Establishes It.

OrpheLink handles the control plane — identities, devices, policies, topology, and auditability. OrpheAgent handles the data plane, establishing encrypted P2P connections after authorization.

  1. 1

    Join OrpheLink

    Add OrpheAgent devices to your control plane

  2. 2

    Verify Device Trust

    Validate device identities and relationships

  3. 3

    Assign Topology & Roles

    Add devices into your network structure

  4. 4

    Establish P2P Connections

    Create encrypted P2P connections automatically

  5. 5

    Monitor & Audit

    Track devices and connection activity

OrpheLink

Control Plane
Manage Connectivity and Access

Centralize authentication, devices, ACLs, connection policies, topology, and audit data.

Decides who can connect and what they can reach.

OrpheAgent

Data Plane
Establish Secure Device-to-Device Connectivity

Runs on devices and systems, establishing encrypted P2P connections after OrpheLink authorization.

Application data bypasses OrpheLink for privacy, low latency, and high performance.

Explore OrpheAgent
Control-Plane Design Principles

Manage Identities, Devices, Policies, and Topology in One Control Plane

As enterprises connect distributed teams, multi-site devices, AI systems, and hybrid infrastructure, the hard part is not just creating a tunnel — it is continuously knowing who, on which device, is allowed to reach what.

OrpheLink centralizes identities, devices, access policies, and topology while separating control from application data, reducing exposure and dependency on centralized traffic gateways.

Core design principles:

  • Zero Exposure by Design
  • Zero Trust Access Control
  • Separate Control & Data Planes
  • Full On-Prem Ownership
OrpheLink centrally manages Zero Trust connectivity for enterprise users, sites, devices, and internal systems
  • Full Control Over Remote Access

    Centralize identity, access policies, and topology. Gain full visibility, control, and auditability across every connection.

  • Private Deployment, Your Way

    Deploy in the cloud, hybrid environments, or fully on-prem while keeping your data and configurations within your own infrastructure.

  • Hidden from Scanning and Attacks

    No exposed entry points, fixed IPs, or open ports — reducing your attack surface and making systems harder to discover and target.

From Planning to Go-Live

Two engines for zero-touch deployment

Use Templates to standardize deployment designs, then let Auto Provision automatically enroll and configure devices. From multi-site planning to device startup, reduce repetitive setup and on-site IT involvement so devices can enter service faster.

Templates network deployment template icon

Define Once, Apply Network-Wide

Centrally define node policies and allowlists, then roll out consistent deployment designs across sites in batches to reduce repetitive work and manual configuration errors.

  • Node policies and allowlists
  • Visual Network Topology
  • Batch Rollout Across Sites
Auto Provision device enrollment and configuration icon

Power On, Connect, and Auto-Provision

Once powered on, devices automatically register and apply their settings. NAT traversal helps them get online quickly without IT staff needing to configure each device on site.

  • Zero-Touch Deployment
  • No On-Site IT Required
  • Automatic NAT Traversal

Auth Connect

Verify Devices and Identities, Then Grant Only Necessary Access

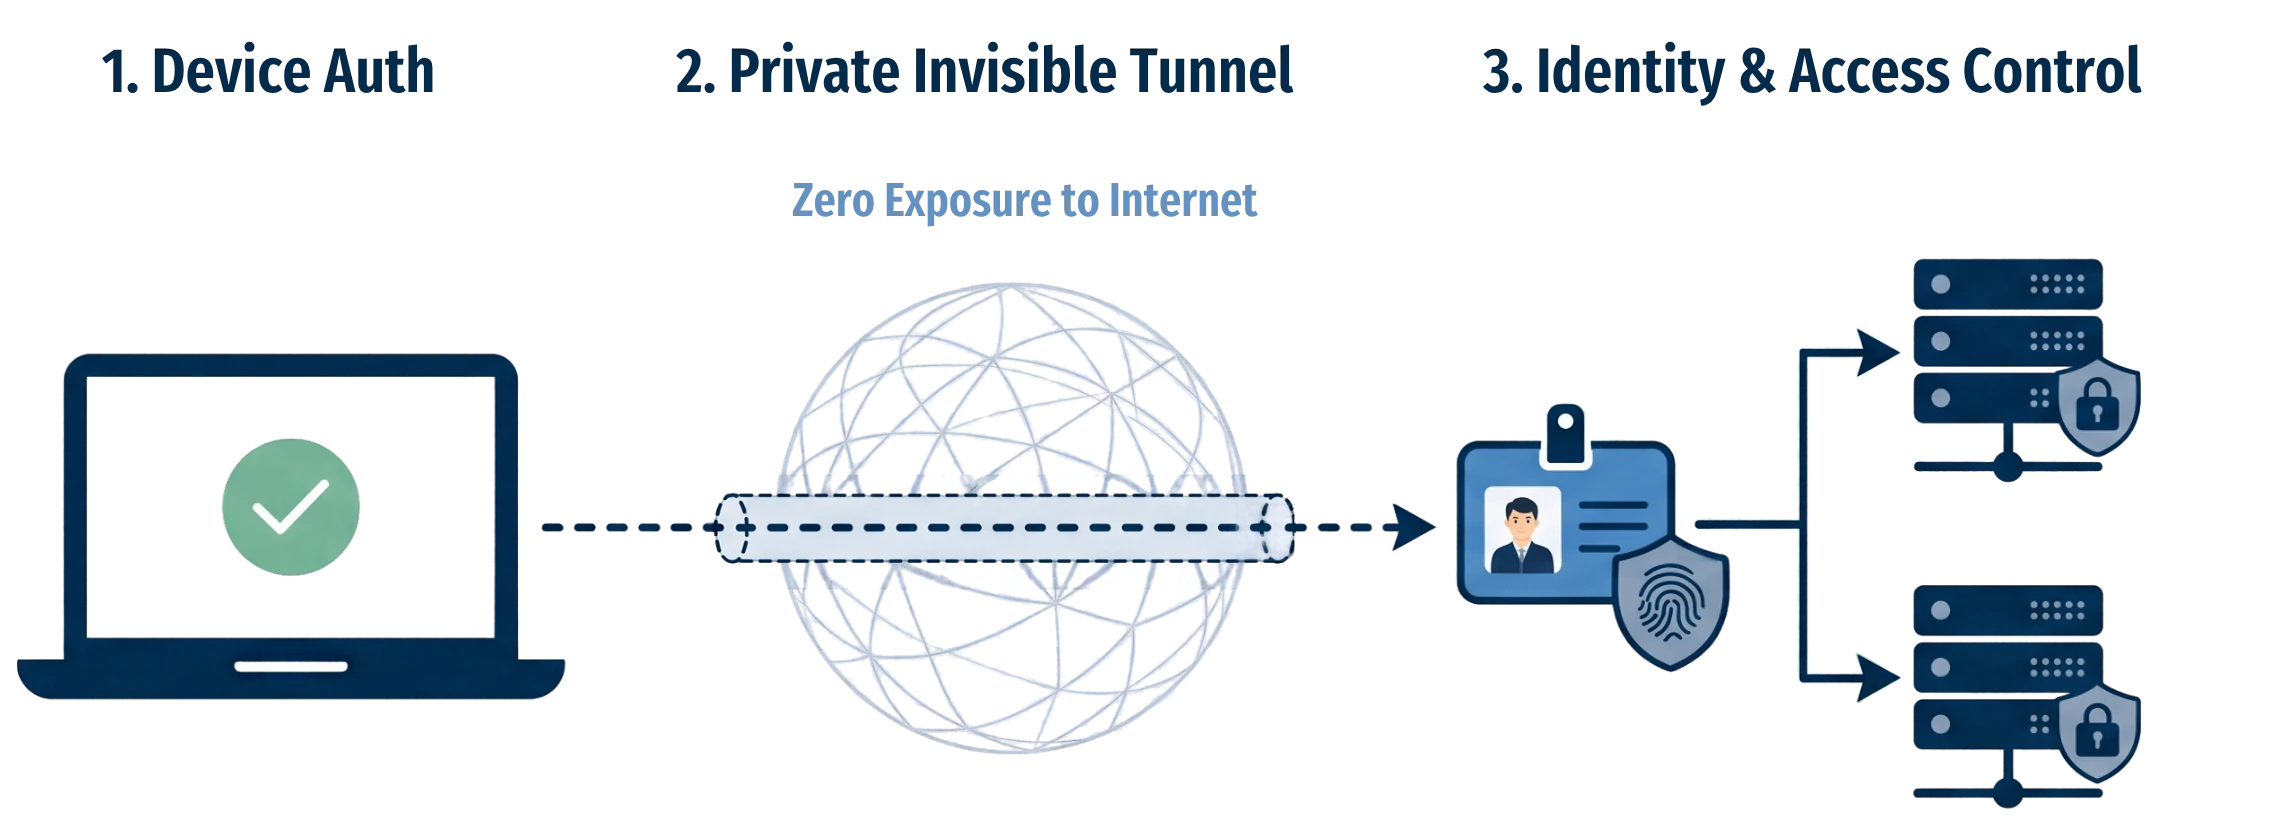
Auth Connect combines device authorization, encrypted network paths, and identity-based access policies. Remote devices reach enterprise resources within approved permissions, reducing public exposure and excessive access.

  • Authorized devices

    Use device authorization and hardware trust as the basis for network enrollment.

  • Less public exposure

    No fixed public IP or open inbound ports required, reducing exposure through public entry points.

  • Least-privilege access

    Assign permissions by role and department, granting access only to resources needed for work.

Auth Connect architecture: authorized devices use device authentication and a private encrypted tunnel with identity and access controls to reach enterprise resources
Select the image to view the full-size diagram
  • Device Authentication

    Verify device authorization and hardware trust before admitting authorized devices to the managed network, providing a basis for subsequent access decisions.

  • Private Invisible Tunnel

    Establish an encrypted network path without a fixed public IP or open inbound ports, helping reduce public exposure of devices and services.

  • Identity & Access Control

    Integrate AD/RADIUS and MFA authentication according to your integrations and policy settings. Grant the minimum permissions needed by role or department to limit resource access.

OrpheLink Core Capabilities

Manage Access, Node Roles, and Topology from One Control Platform

OrpheLink gives enterprises control over how devices join, which roles they perform, what resources they can reach, and how the overall topology operates.

Flexible Connectivity Architecture

Support multiple topologies and node configurations across different environments.

  • P2P Connections
  • Centralized Traffic Egress
  • Site-to-Site

Built for multi-site and hybrid environments.

Configurable Node Roles

Assign different node roles so devices can act as relays, exit nodes, or site-to-site connections.

  • Node
  • Exit Node
  • Route to Exit Node
  • Relay Node

Create clearer network boundaries and access controls.

Fine-Grained Access Control (ACL)

Define access rules based on identities, devices, and policies.

Identity-Based Access
Device-Based Access

Enforce least-privilege access and network isolation.

Complete Network Visibility

Gain centralized visibility into devices, connection status, and network relationships.

OrpheLink site topology management interface

See your network structure and connectivity at a glance.

Deploy Your Way

Choose the deployment model that fits your infrastructure, security, and operational requirements.

  • Cloud
  • Fully On-Prem
  • Hybrid

From cloud to fully on-prem, stay in control of your data and environment.

Separate Control & Data Planes

OrpheLink manages control and access policies while traffic flows directly between devices.

OrpheLink separates its control plane from device-to-device data traffic

Private by design with low-latency, high-performance connectivity.

Ready for AI workloads, global operations, and distributed environments.

  • Stronger Security
  • Greater Flexibility
  • Simplified Management

Deploy Without Rebuilding Your Network

Integrate OrpheLink into your existing infrastructure with minimal changes.

  1. Step 1

    Choose Your Deployment

    Cloud, hybrid, or fully on-prem.

  2. Step 2

    Add Devices and Nodes

    Bring devices and sites into OrpheLink for centralized visibility and control.

  3. Step 3

    Define Access Policies

    Control access with ACLs, identity-based policies, and network rules.

Deploy OrpheLink with minimal infrastructure changes.

Architecture Validation

Compared with Traditional Centralized Remote Access, OrpheLink Changes the Control Model

Compared with Traditional Centralized Remote Access, OrpheLink Changes the Control Model
FeatureOrpheLinkTraditional Remote Access
ExposureNo public infrastructure requiredFixed IPs and exposed ports
ArchitectureSeparate control and data planesShared entry point for management and traffic
DeploymentCloud, hybrid, or fully on-premOften dependent on third-party infrastructure
Access ControlIdentity and policy-based accessLimited controls after network access
OwnershipFully self-managedReliant on external platforms and services

The goal is not only to connect devices, but to reduce exposure while preserving centralized control, authorization, and deployment autonomy.

Build a Zero Exposure, Zero Trust Remote Access Environment

No public IPs, VPN gateways, or open ports required. Deploy and manage enterprise remote access in minutes.

Start for Free Contact Sales
  • Technical Support

    Deployment guidance and technical assistance from our team.

  • Enterprise-Grade Security

    Built to meet enterprise security and compliance requirements.

  • Flexible Integration

    Easily integrate with your existing systems and infrastructure.

  • Global Deployment Support

    Built for global enterprises and distributed organizations.

O'Prueba Logo

© 2026 O'Prueba Technology Inc. All rights reserved.

Products

  • OrpheLink
  • OrpheAgent

Resources

  • News
  • Use Cases
  • Blog
  • Manual

Company

  • About Us
  • Contact Us
  • Privacy Policy
  • Cookie Policy

Follow Us

  • LinkedIn
  • Facebook
  • YouTube