Hidden from Exposure
Devices stay invisible to public networks without public IPs or exposed ports.
A P2P Secure Connectivity Agent for Endpoints
OrpheAgent runs on desktops, servers, mobile devices, and edge systems. After OrpheLink authorization, it establishes encrypted P2P connections with other nodes.
Application data does not need to traverse OrpheLink or a centralized VPN gateway, preserving privacy, low latency, and a smaller external attack surface.
OrpheAgent handles application connectivity, while OrpheLink manages identities, devices, roles, and access policies. Control stays centralized while data flows directly.
Install OrpheAgent on desktops, servers, or mobile devices.
Bring devices into OrpheLink for centralized management and connectivity control.
Authorized devices establish direct encrypted peer-to-peer connections without relays or gateways.
Authorized devices establish direct encrypted P2P connections without relays or gateways.
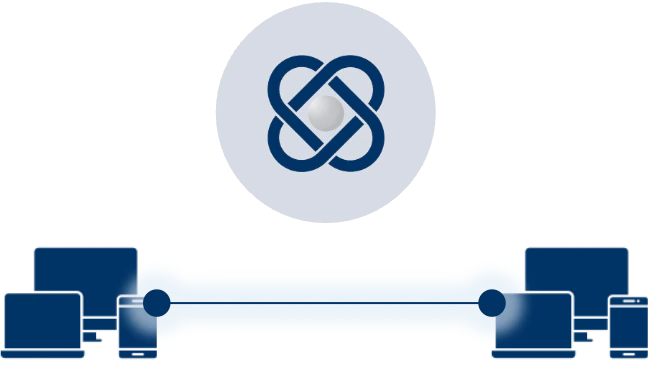
Secure P2P Connectivity Established
OrpheAgent establishes connectivity. OrpheLink manages it.
Security Properties of Every Connection
OrpheAgent does not require devices to expose permanent public entry points. Each connection is authorized through OrpheLink before endpoints establish an encrypted P2P path, with PQC capabilities for stronger long-term cryptographic resilience.
Devices stay invisible to public networks without public IPs or exposed ports.
Every connection is authenticated and access-controlled with least-privilege enforcement.
Devices connect directly through encrypted P2P tunnels without routing traffic through third-party relays.
Built with post-quantum cryptography to strengthen protection against future threats.
Not every device needs the same networking capabilities. OrpheAgent Standard and Lite let core nodes and general endpoints use different connectivity models.
Standard fits core devices that need Full Mesh, Exit Node, or LAN-to-LAN capabilities. Lite is designed for large fleets of employee and external-collaboration endpoints.
Both editions can coexist in the same OrpheLink environment so each device receives the capabilities appropriate to its role.
| Feature | Standard | Lite |
|---|---|---|
| Topology | Full Mesh P2P | Hub-and-Spoke |
| Connectivity | Direct connectivity between authorized nodes | Connects to a designated node only |
| Exit Node | Supported | Not supported |
| Route via Exit Node | Supported | Supported |
| LAN-to-LAN | Supported | Not supported |
| Best For | Multi-site environments, core infrastructure, Edge AI, Site-to-Site | Employee devices, partner access, restricted environments |
| Deployment Focus | Full connectivity and advanced networking | Simplified deployment at scale |
No Network Changes Required
OrpheAgent works with your existing infrastructure and devices without requiring public IPs, VPN redesigns, or hardware replacement. Deploy across desktops, mobile devices, servers, NAS systems, AI/GPU infrastructure, and edge environments — all within a unified secure connectivity architecture.
From remote access and AI/GPU infrastructure connectivity to Zero Trust deployment planning, our team can help you design and deploy the right architecture for your environment.
We Can Help With
Product Demo
Deployment Planning
Pricing Consultation
Technical Consultation
Deployment guidance and technical assistance from our team.
Built to meet enterprise security and compliance requirements.
Easily integrate with your existing systems and infrastructure.
Built for global enterprises and distributed organizations.