OrpheLink
Learn about OrpheLink features, including Site-to-Site connections, LAN-to-LAN connections, and setting up exit nodes securely.
OrpheLink provides several key features to ensure secure and flexible connectivity:
- Site-to-Site Connection: Establishes a secure connection between different physical or logical sites.
- LAN-to-LAN Connection: Connects Local Area Networks across different locations.
- Exit Node: Allows you to designate an exit node to route traffic through specific nodes.
All connections between nodes utilize TLS 1.3 and QUIC protocols, ensuring a high level of security.
OrpheLink uses a three-layer topology architecture. Administrators can move from a site-wide overview down to an individual node's connections and control routing and security at the appropriate layer.
Layer 1: Site Topology
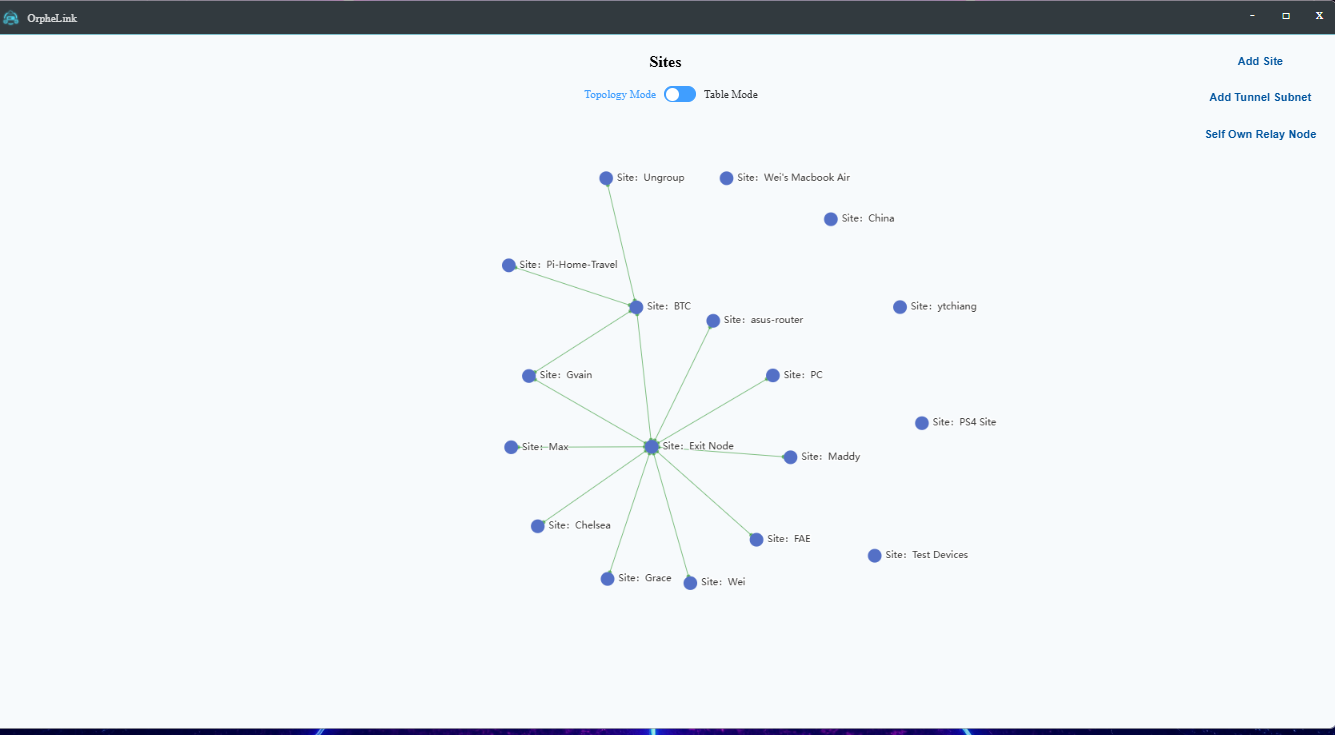
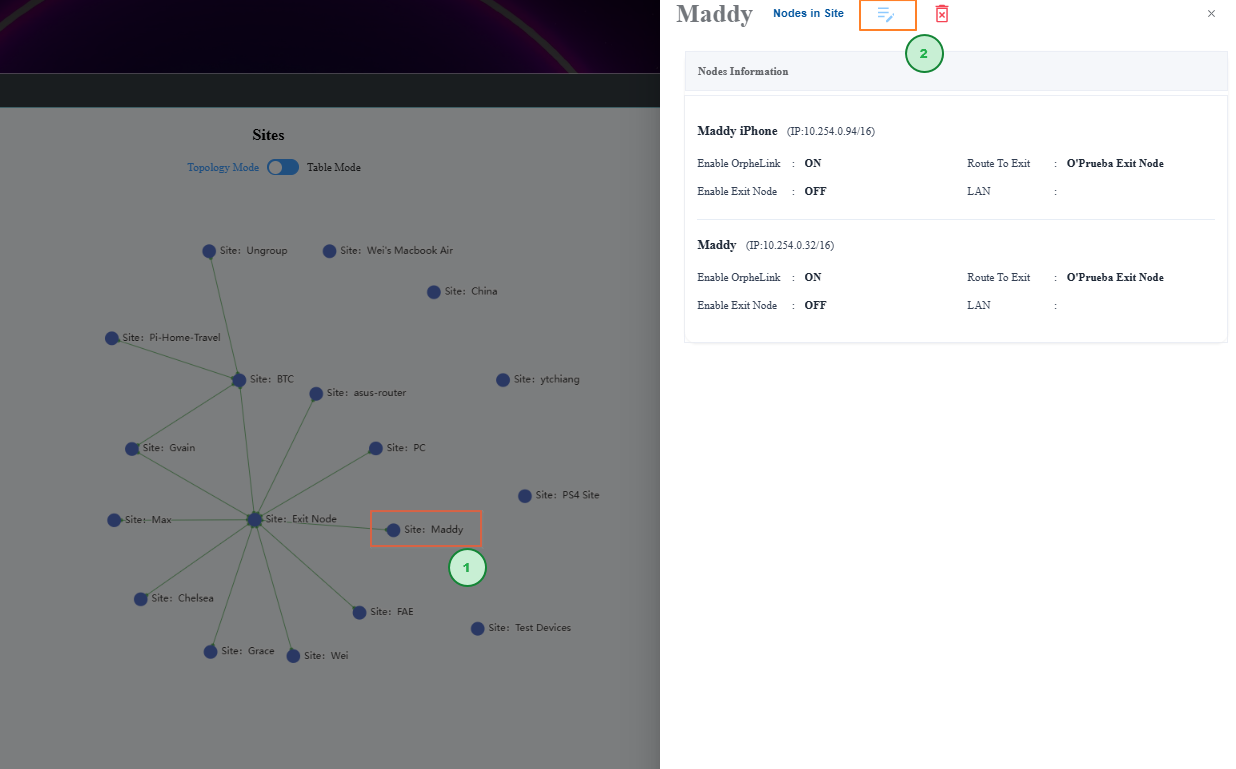
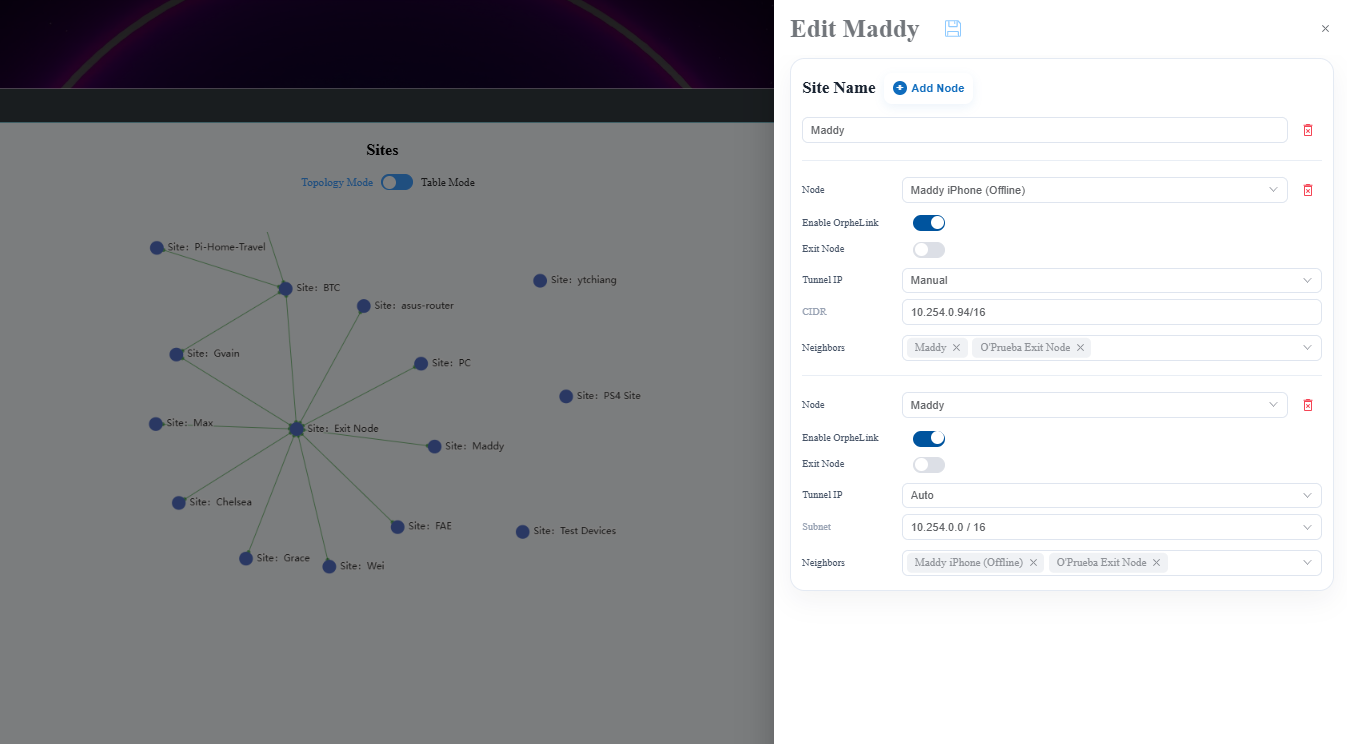
The Site Topology view presents the overall network blueprint. From this view, you can create sites, register nodes, control connection behavior after startup, configure local routing policies, track inter-node tunnels, and view discovered local networks. Click Edit to change node behavior, advanced routing policies, and network bypass rules.
| Name | Description |
|---|---|
| Topology of Site | Displays the current sites and their connections. |
| Add Tunnel Subnet | Creates a tunnel subnet range for the overlay network. When a node's Tunnel IP is set to Auto, OrpheLink allocates an address from this range for its P2P connection. |
| Add Self Own Relay node | Creates a self-hosted relay node with a public IP and configurable transmission rate limits. |
| Add site | Creates a site, assigns nodes, designates an exit node and Tunnel IPs, defines neighbor connections, and adds LANs. |
| Enable OrpheLink | When enabled, the node automatically establishes its P2P connection after a restart. When disabled, the connection must be established manually after a restart. |
| Exit node | Designates the node as an exit point. Nodes with Route to Exit enabled send their traffic through this exit node before it is forwarded. |
| SNAT | Appears only when Exit Node is enabled. Enabling SNAT masks internal source IPs behind the exit node for plug-and-play connectivity. Disabling it preserves original device IPs so upstream firewalls can perform granular traffic auditing. |
| Tunnel Subnet / Tunnel IP | Defines the virtual CIDR range used for internal P2P routing. Auto lets the system allocate addresses to prevent conflicts; Manual lets you specify the CIDR. |
The topology uses the following icons for sites, exit nodes, regular nodes, and clients:
| Type | Icon |
|---|---|
| Site |  |
| Exit node |  |
| Node |  |
| Clients |  |
Layer 2: Nodes in Site
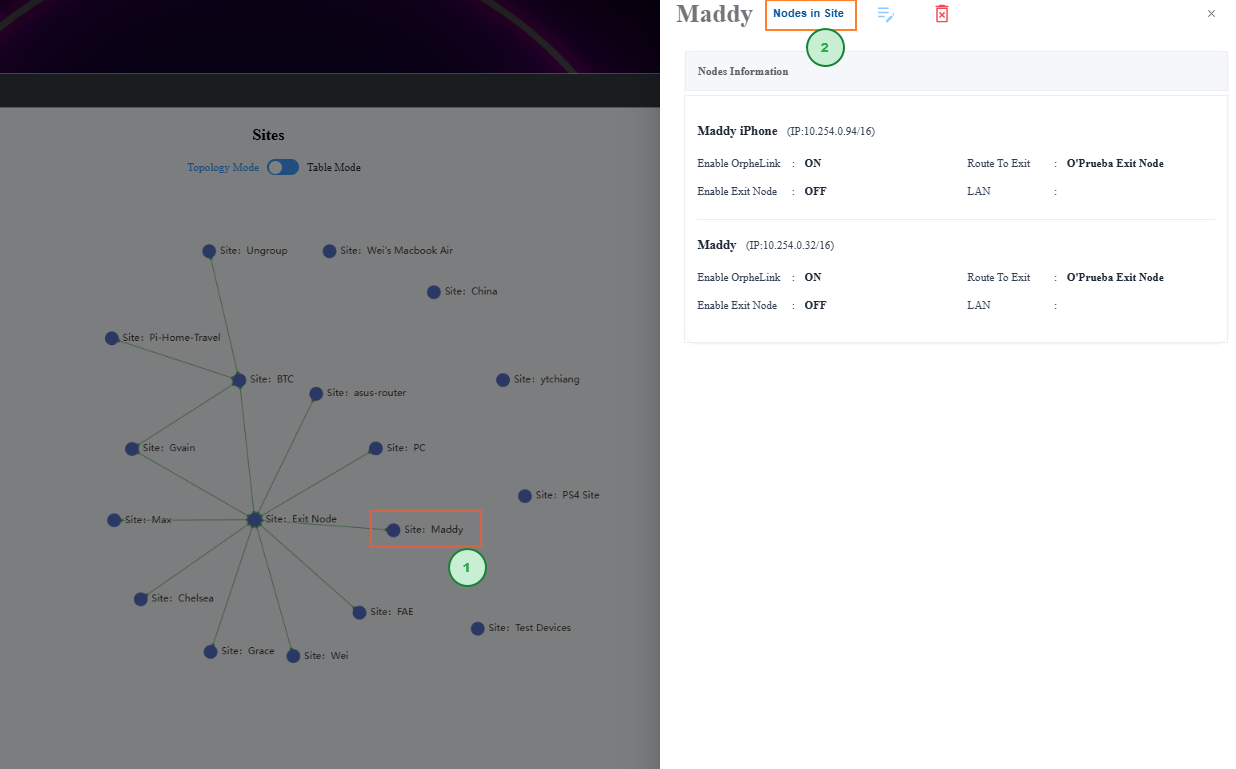
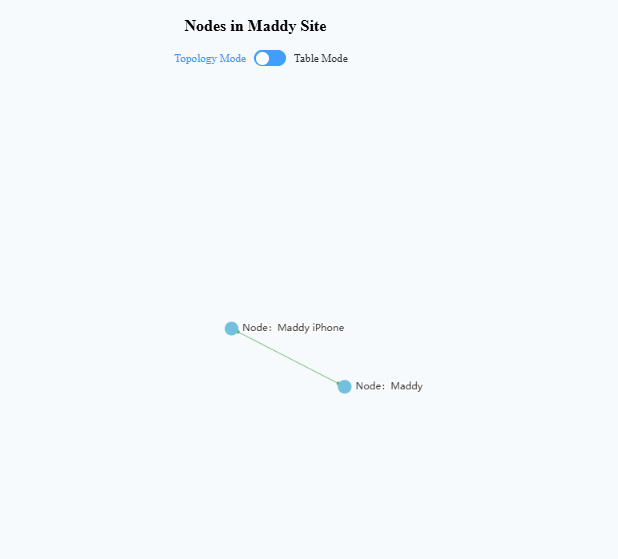
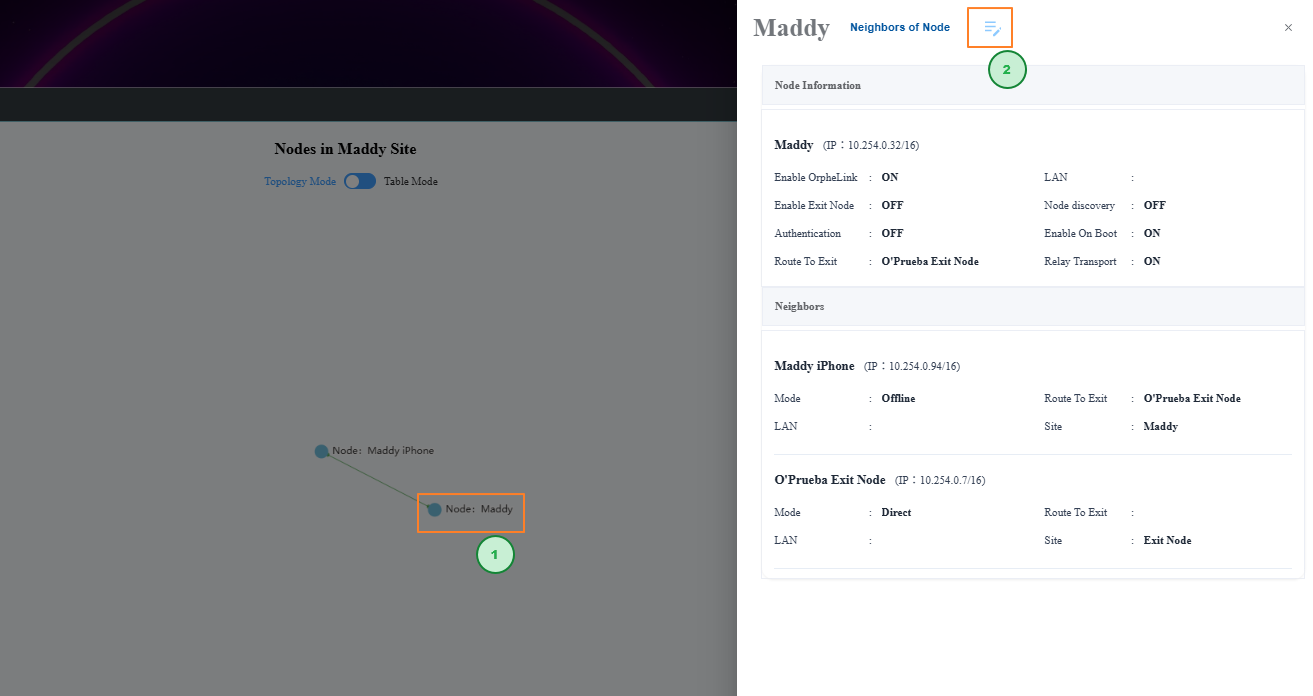
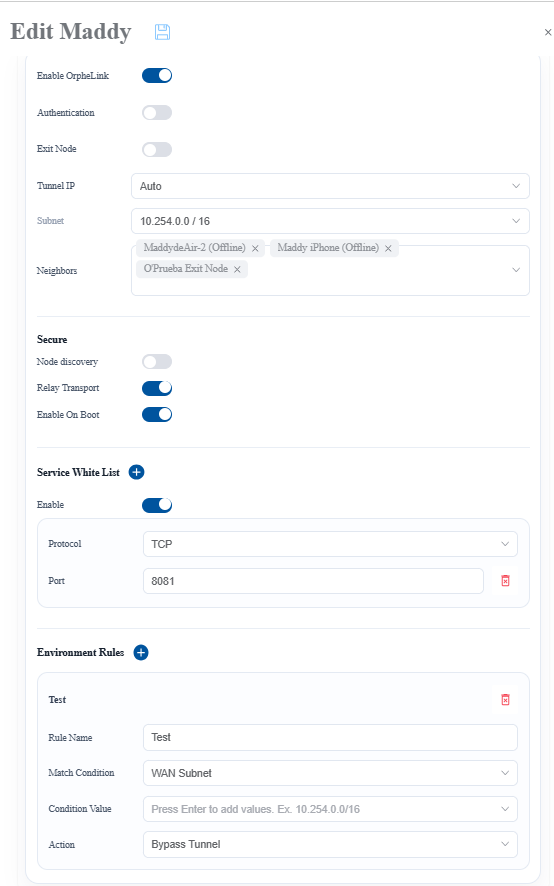
Click Nodes in Site to list every managed node assigned to the site. Hover over or select a node to open its live status panel. Click Edit to configure node behavior, advanced routing policies, and network environment rules.
| Name | Description |
|---|---|
| Enable OrpheLink | Controls data-plane connectivity. On by default, it activates all secure P2P tunnel links. Turning it off suspends P2P communication while leaving the control plane active, so the node remains manageable from the dashboard. |
| Authentication to Access | Enforces zero-trust access. Cross-node access is intercepted by a dynamic login page, and users must authenticate before reaching the node. |
| Node discovery | Enabling it improves NAT traversal, but a firewall may flag the resulting connection as suspicious. When disabled, NAT traversal uses an O'Prueba relay node or a customer-owned relay node. |
| Relay Transport | When enabled, traffic can be forwarded through a relay node if a direct connection fails. When disabled, relay forwarding is not allowed. |
| Enable On Boot | Controls tunnel behavior after a device restarts or powers on. On by default, it restores the P2P connection automatically. When disabled, tunnels remain offline after startup. |
| Service White List | Configures allowed TCP or UDP service ports, such as Remote Desktop, SSH, or web applications. When enabled, only listed ports can communicate between devices, reducing unnecessary network exposure and strengthening SD-WAN security. |
| Environment Rules | Configures a WAN Subnet Bypass Rule for split tunneling. For example, traffic from a branch office at 172.16.1.x to headquarters at 10.10.1.x can continue over an existing VPN instead of the OrpheLink tunnel. |
Layer 3: Neighbor of Node
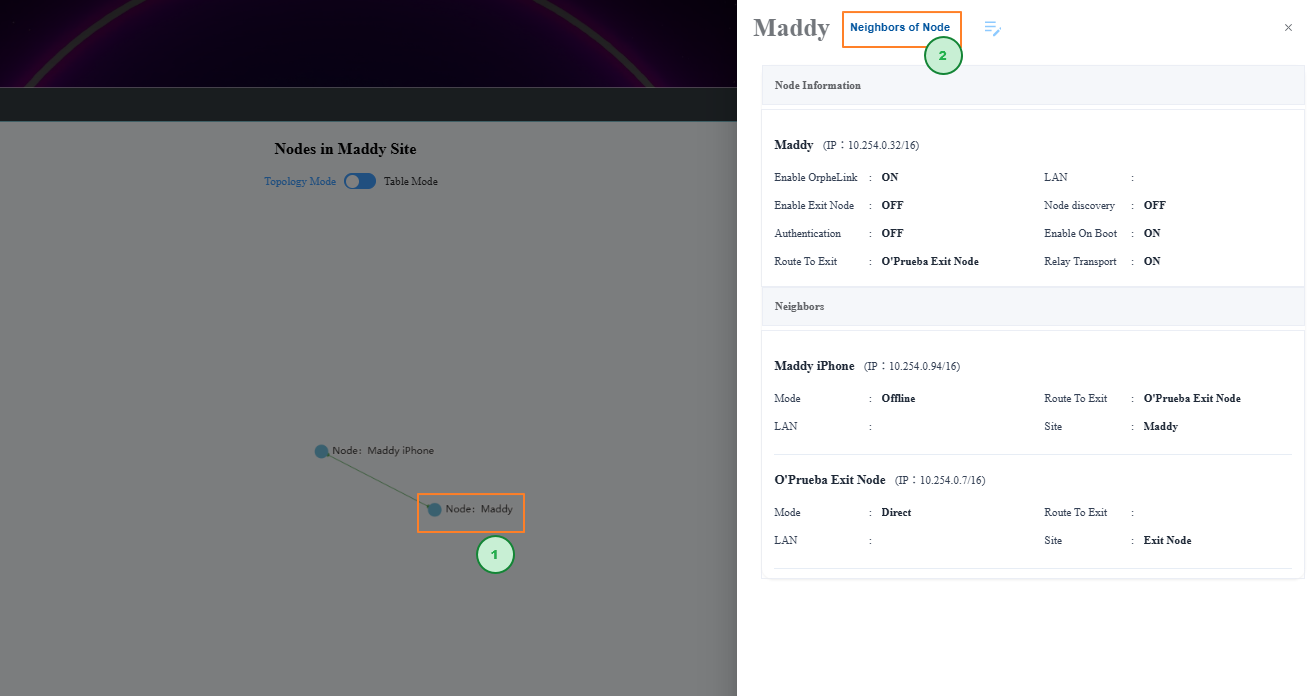
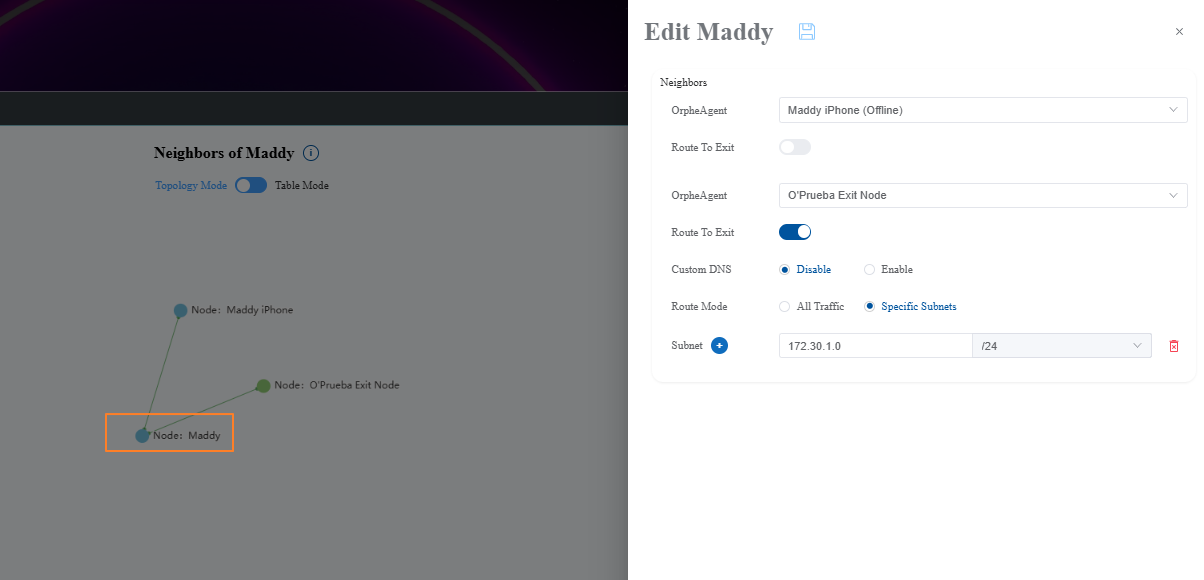
This view focuses on one node's connections. Use it to inspect peers, configure Route to Exit, select a route mode, and apply custom DNS settings.
| Name | Description |
|---|---|
| Neighbors | Displays the peers connected to the selected node. |
| Route to Exit | Select an exit node and enable this option to route device traffic through that specific gateway. |
| Route Mode | All Traffic sends all network traffic through the exit node. Specific Subnets sends only the subnet ranges you define. |
| Custom DNS | Available only in All Traffic mode. When enabled, custom DNS settings are sent and applied to the node; deleting the Link also removes those settings from the device. Disabling it stops custom DNS propagation. |
Setup Scenario
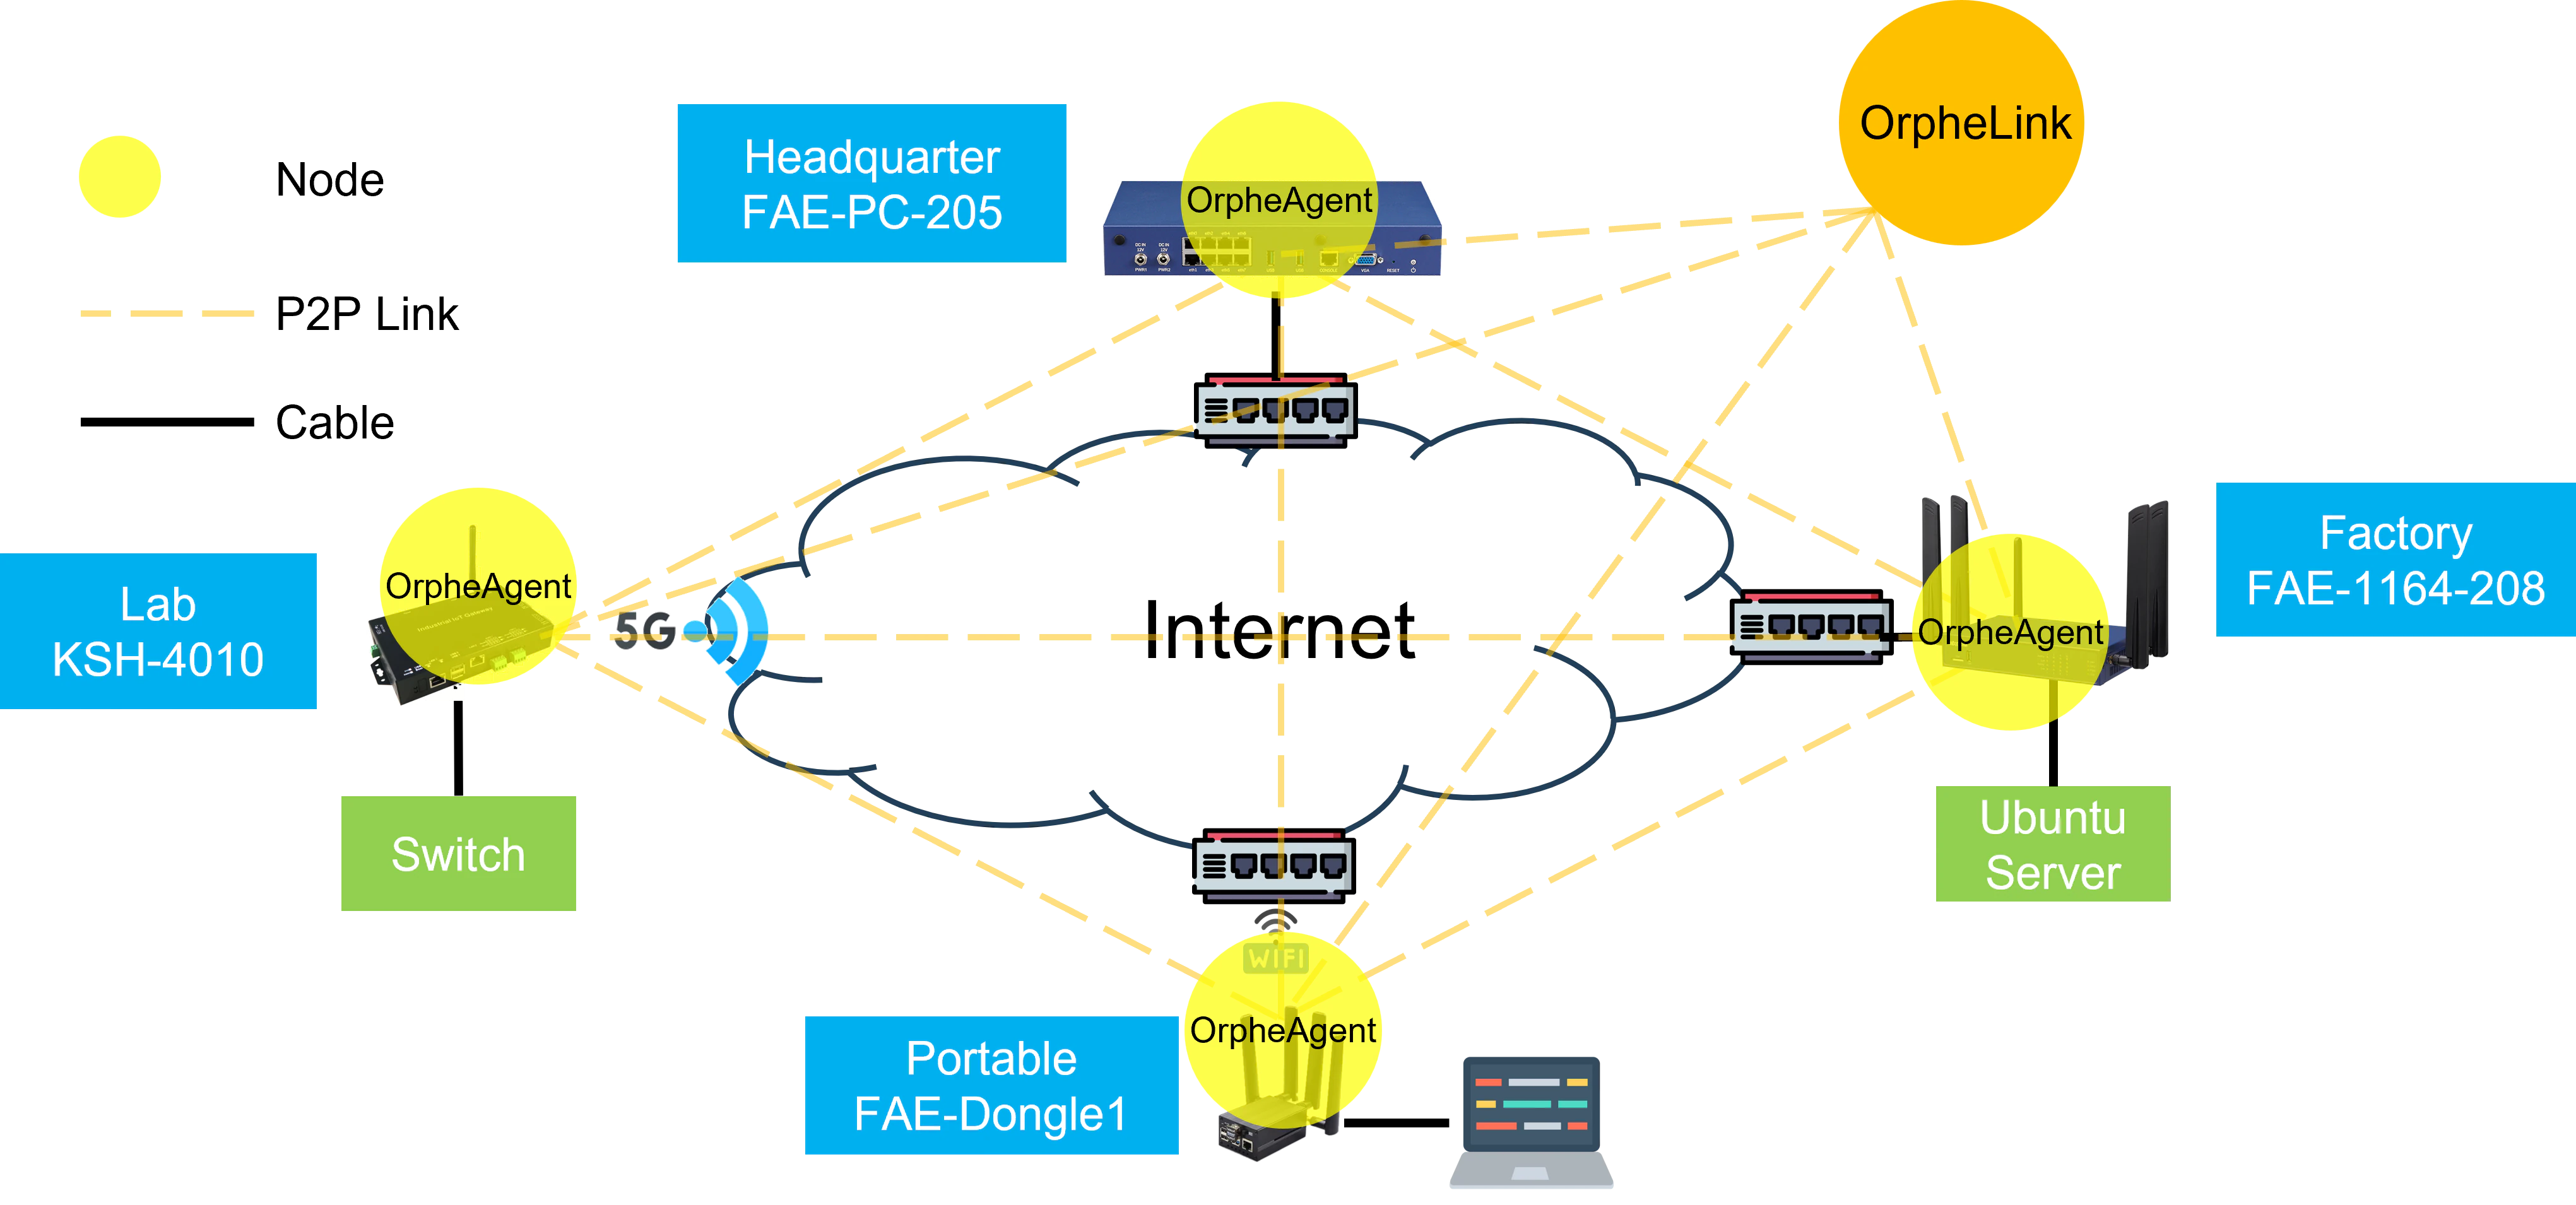
Consider a scenario where devices in different locations (even across different countries) have clients behind NAT with private IP addresses. Using OrpheLink, these devices can communicate securely through a tunnel, enabling direct data transfer across NAT boundaries.
| Location | Name | Agent Type | WAN IP | LAN | Client |
|---|---|---|---|---|---|
| HQ | FAE-1164-208 | Binary | Cable; 192.168.100.74 | 192.168.208.0/24 | Ubuntu 24.04 Server; 192.168.208.2 |
| Lab | KSH-4010 | Container | 5G Network; 10.139.28.25 | 192.168.1.0/24 | EstiNet Switch; 192.168.1.200 |
| Factory | FAE-PC-205 | Container | Cable; 172.30.1.205 | N/A | N/A |
| Portable | FAE-Dongle1 | Binary | Wi-Fi; 192.168.210.6 | 192.168.106.0/24 | Laptop MSI |
Configuration Steps
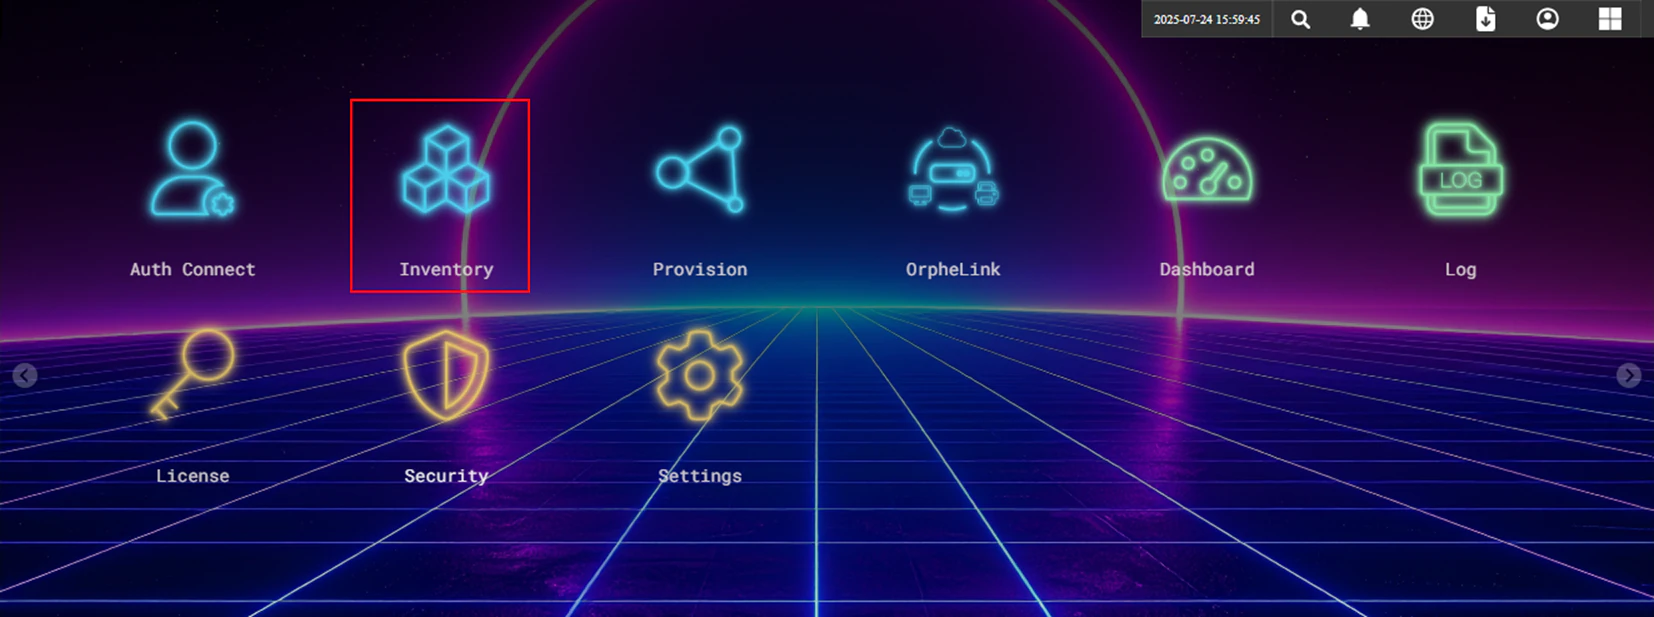
- Log in to OrpheLink and navigate to the Inventory.
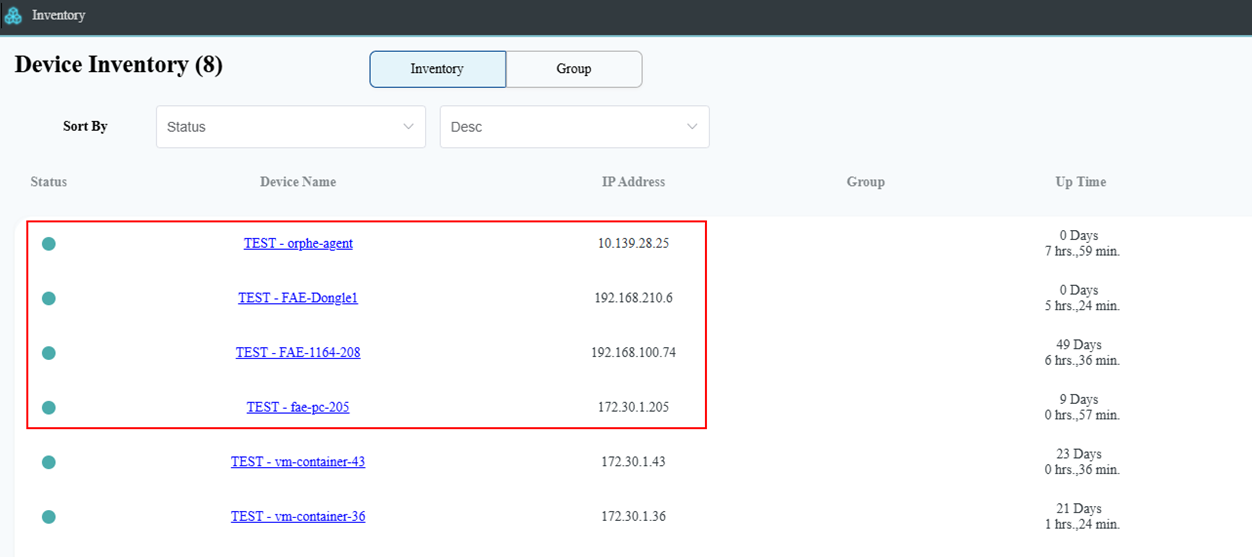
- Verify that your OrpheAgent devices are listed.
- Click the OrpheLink icon to configure links.
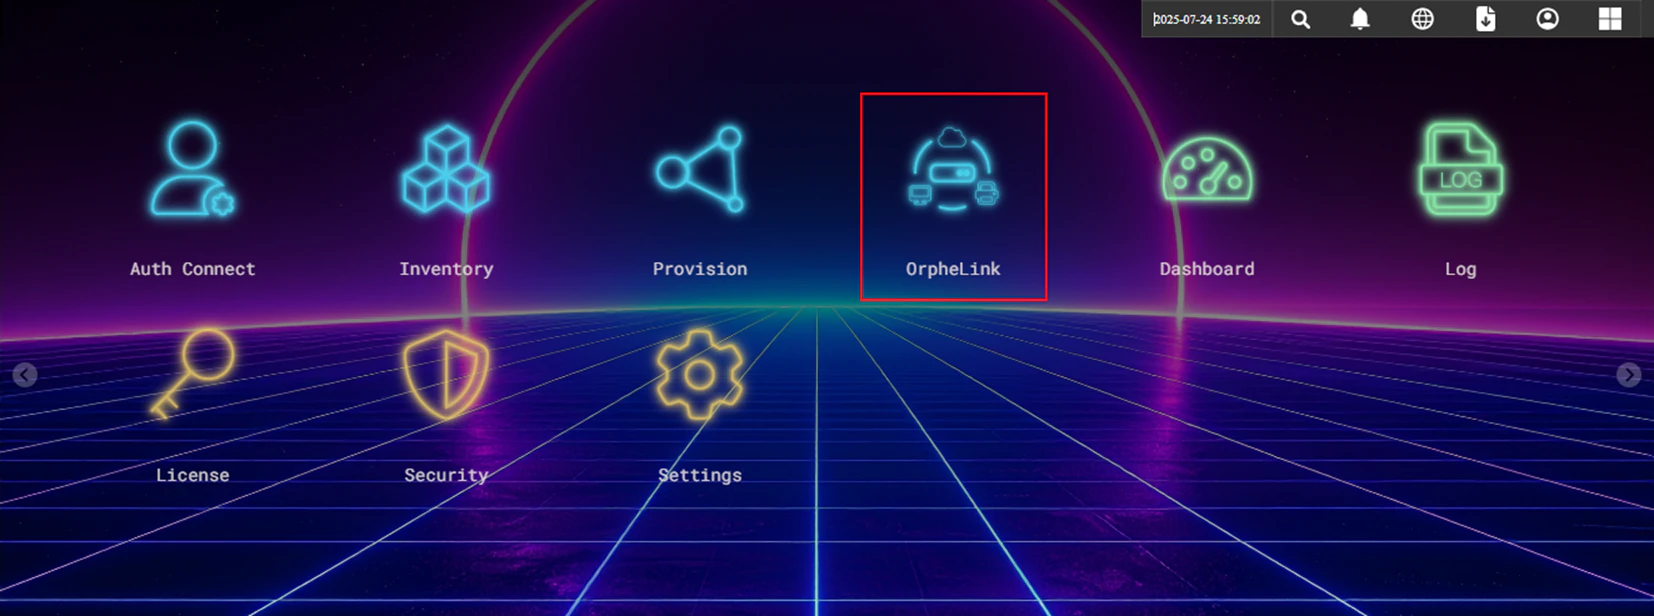
!NOTE Any OrpheAgent devices that have not yet been configured will be placed in the Ungroup site by default.
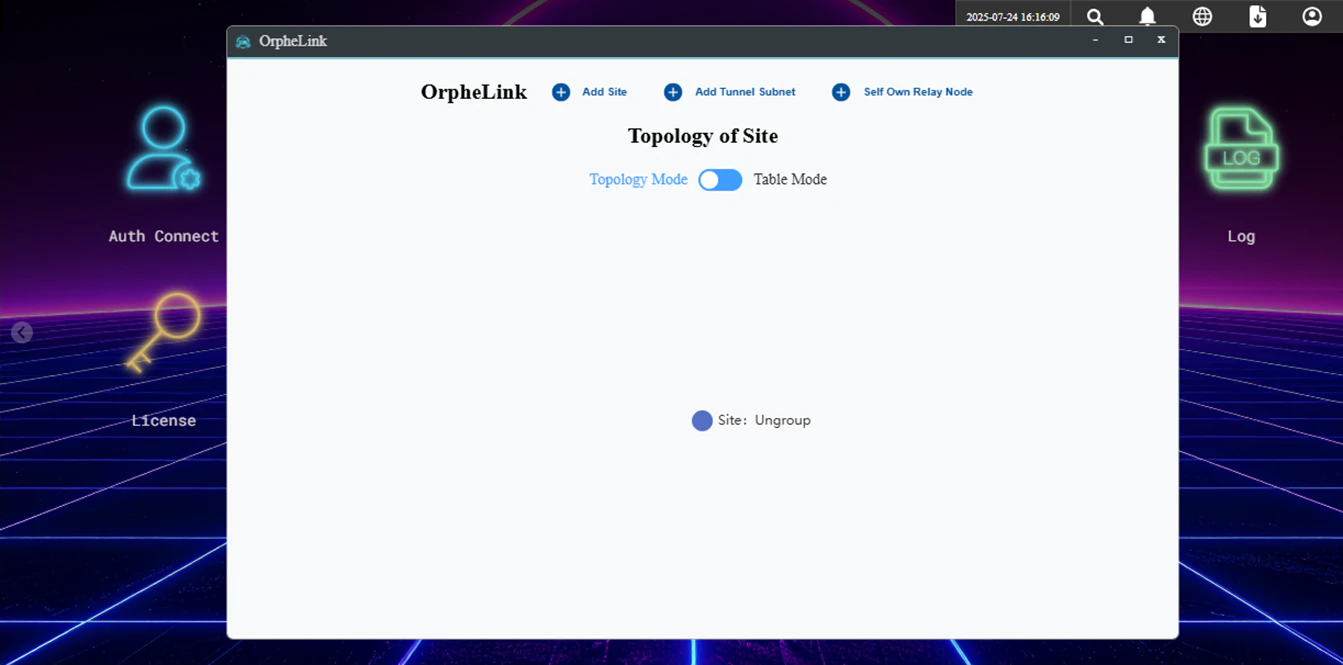
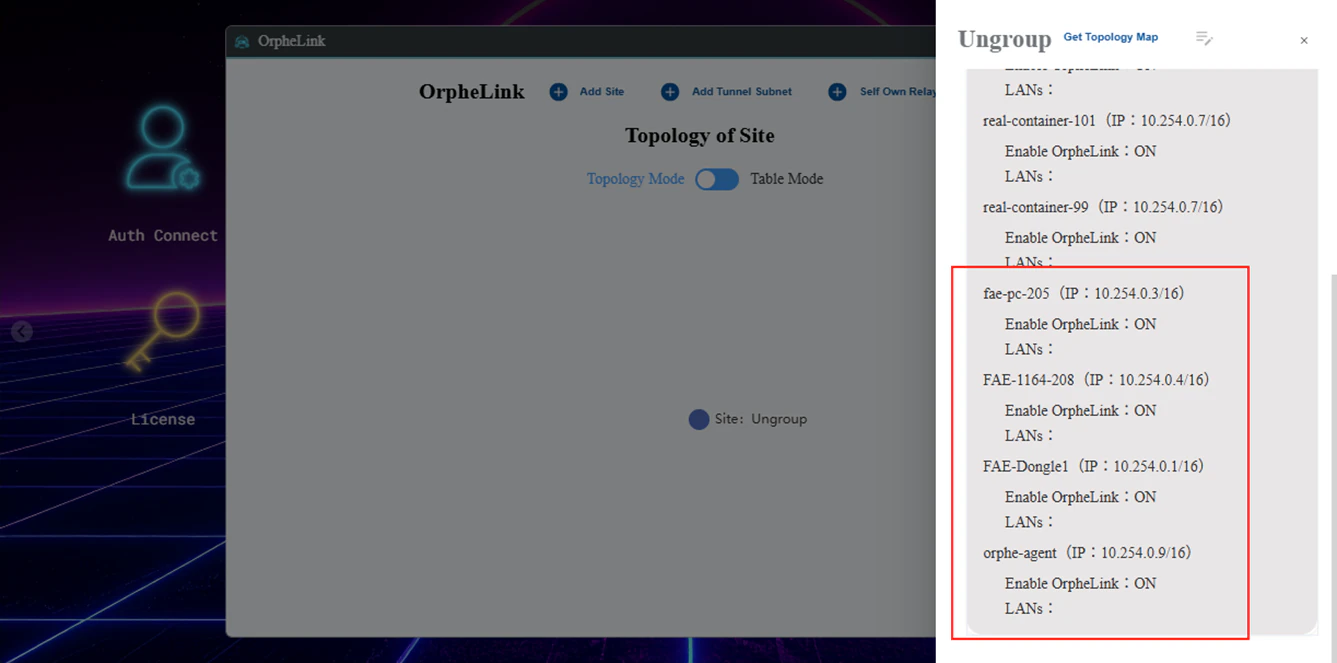
- Click on the Ungroup icon to see the number of OrpheAgent devices inside.
- Click Add site.
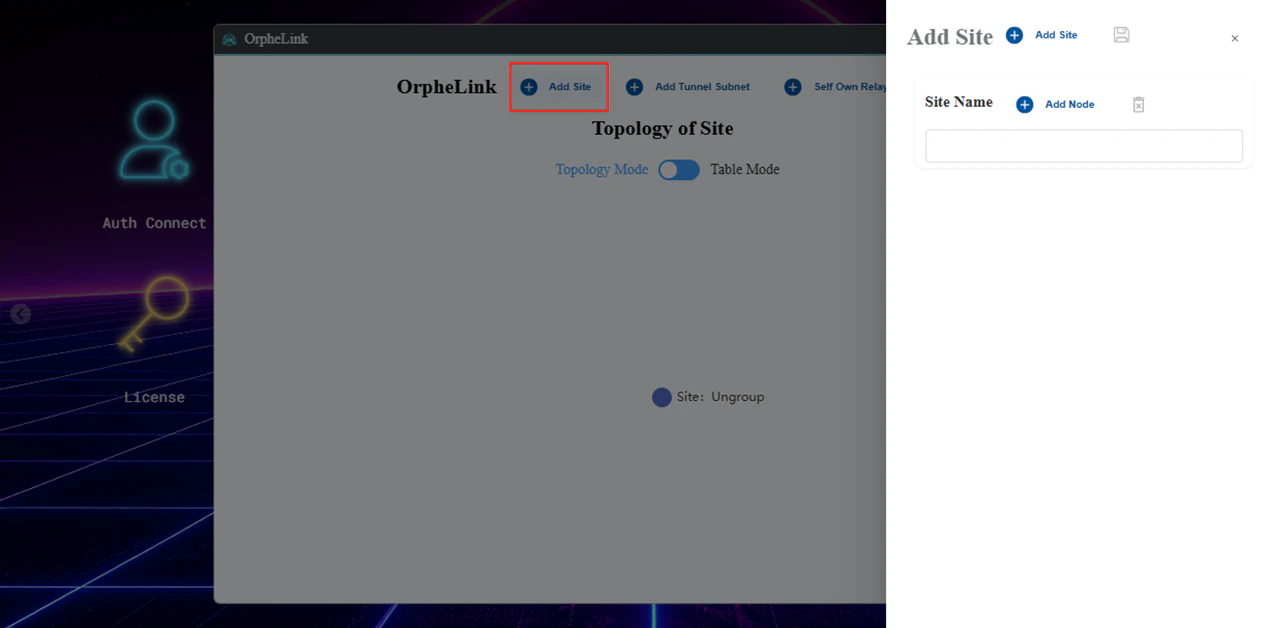
- Add four sites named
HQ,Lab,Factory, andPortable, then click Save.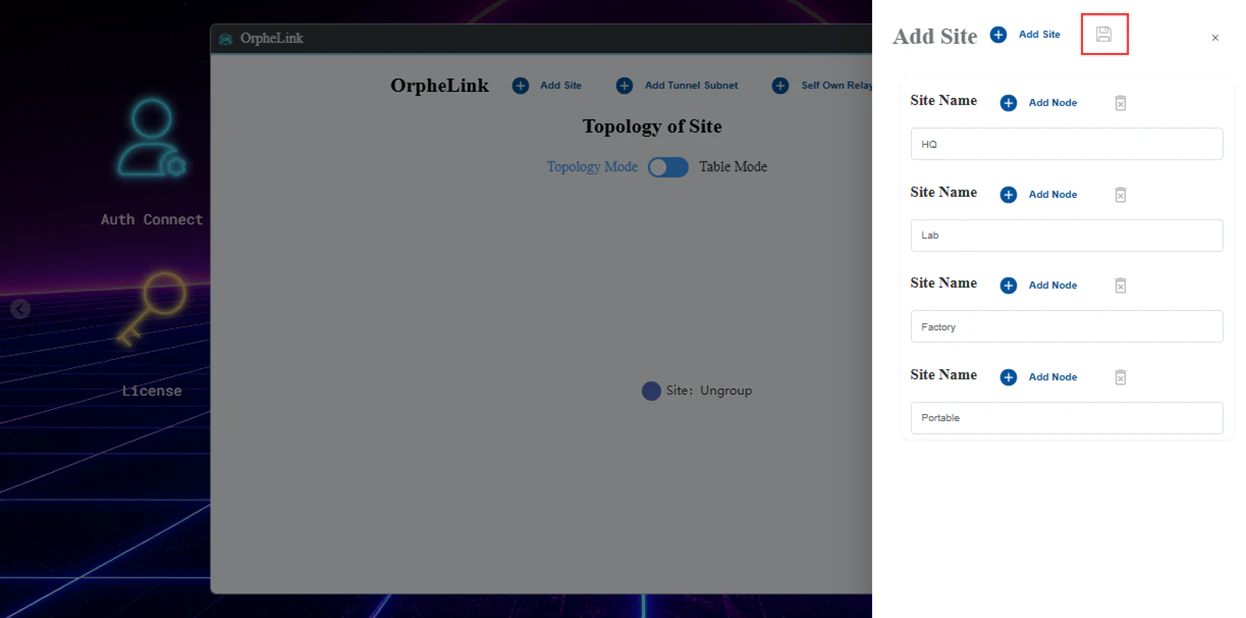
- Click the
HQsite and then click the Edit icon to add a node.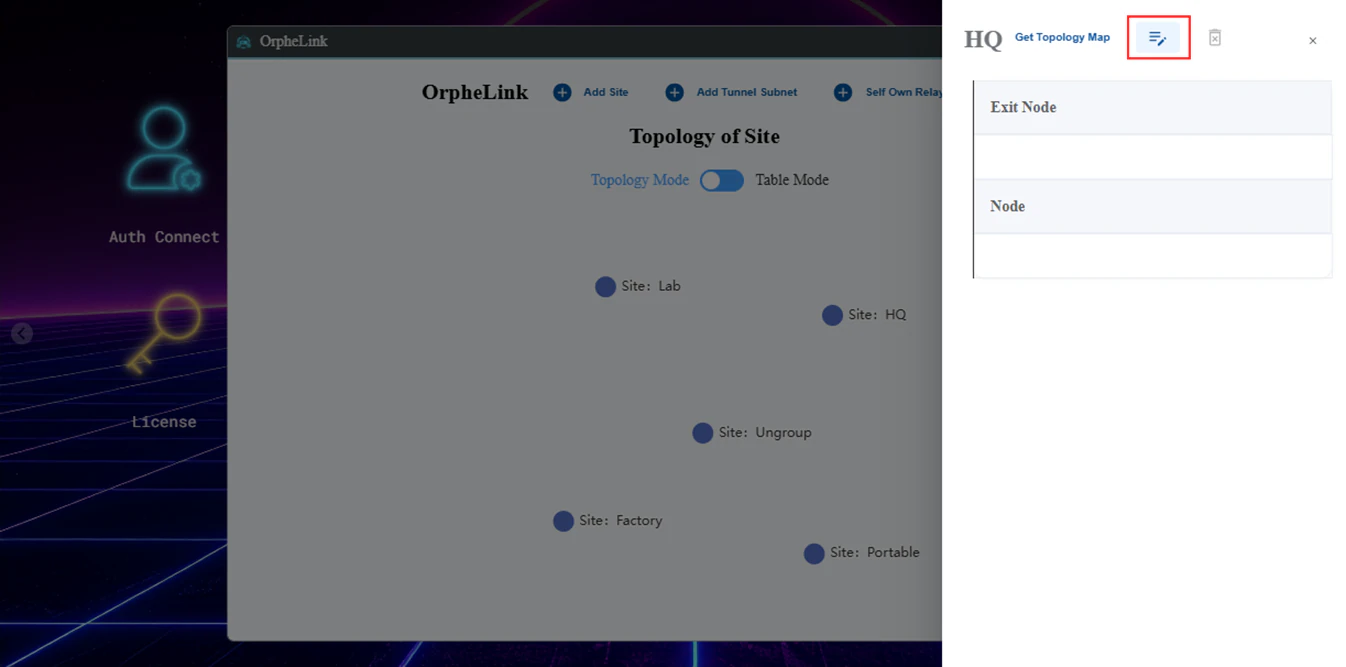
- Click Add Node to add an OrpheAgent device and configure its connections.
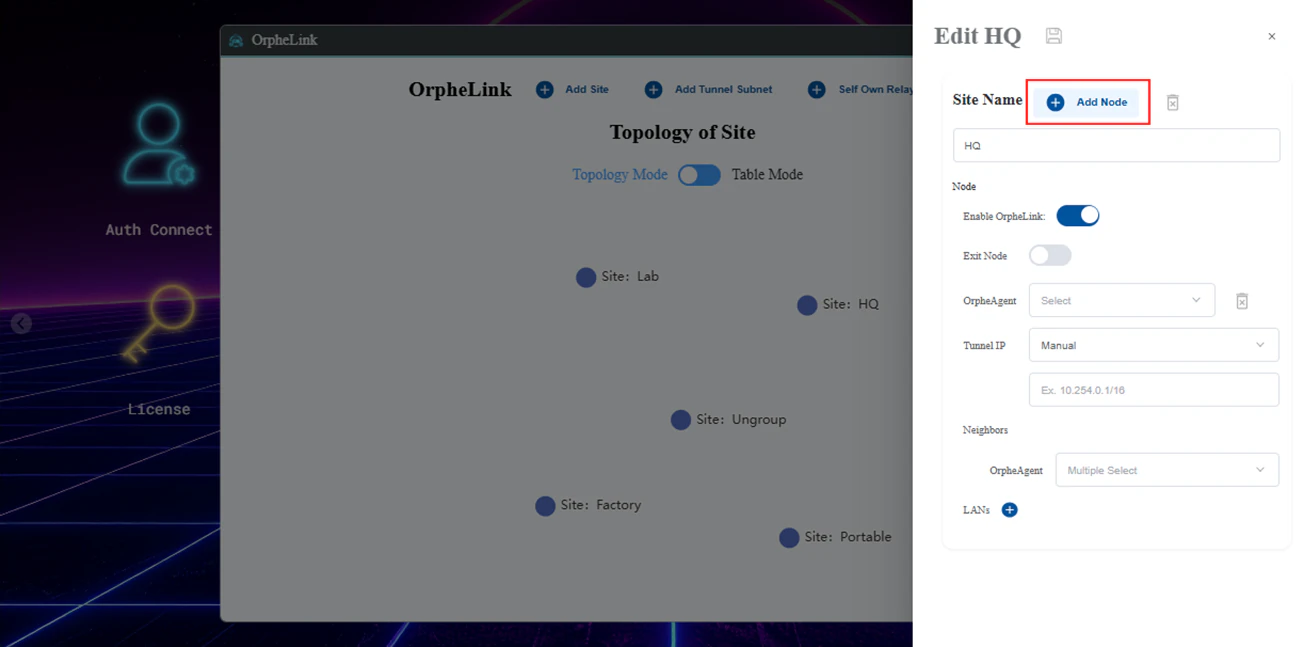
- Choose
FAE-1164-208from the OrpheAgent list.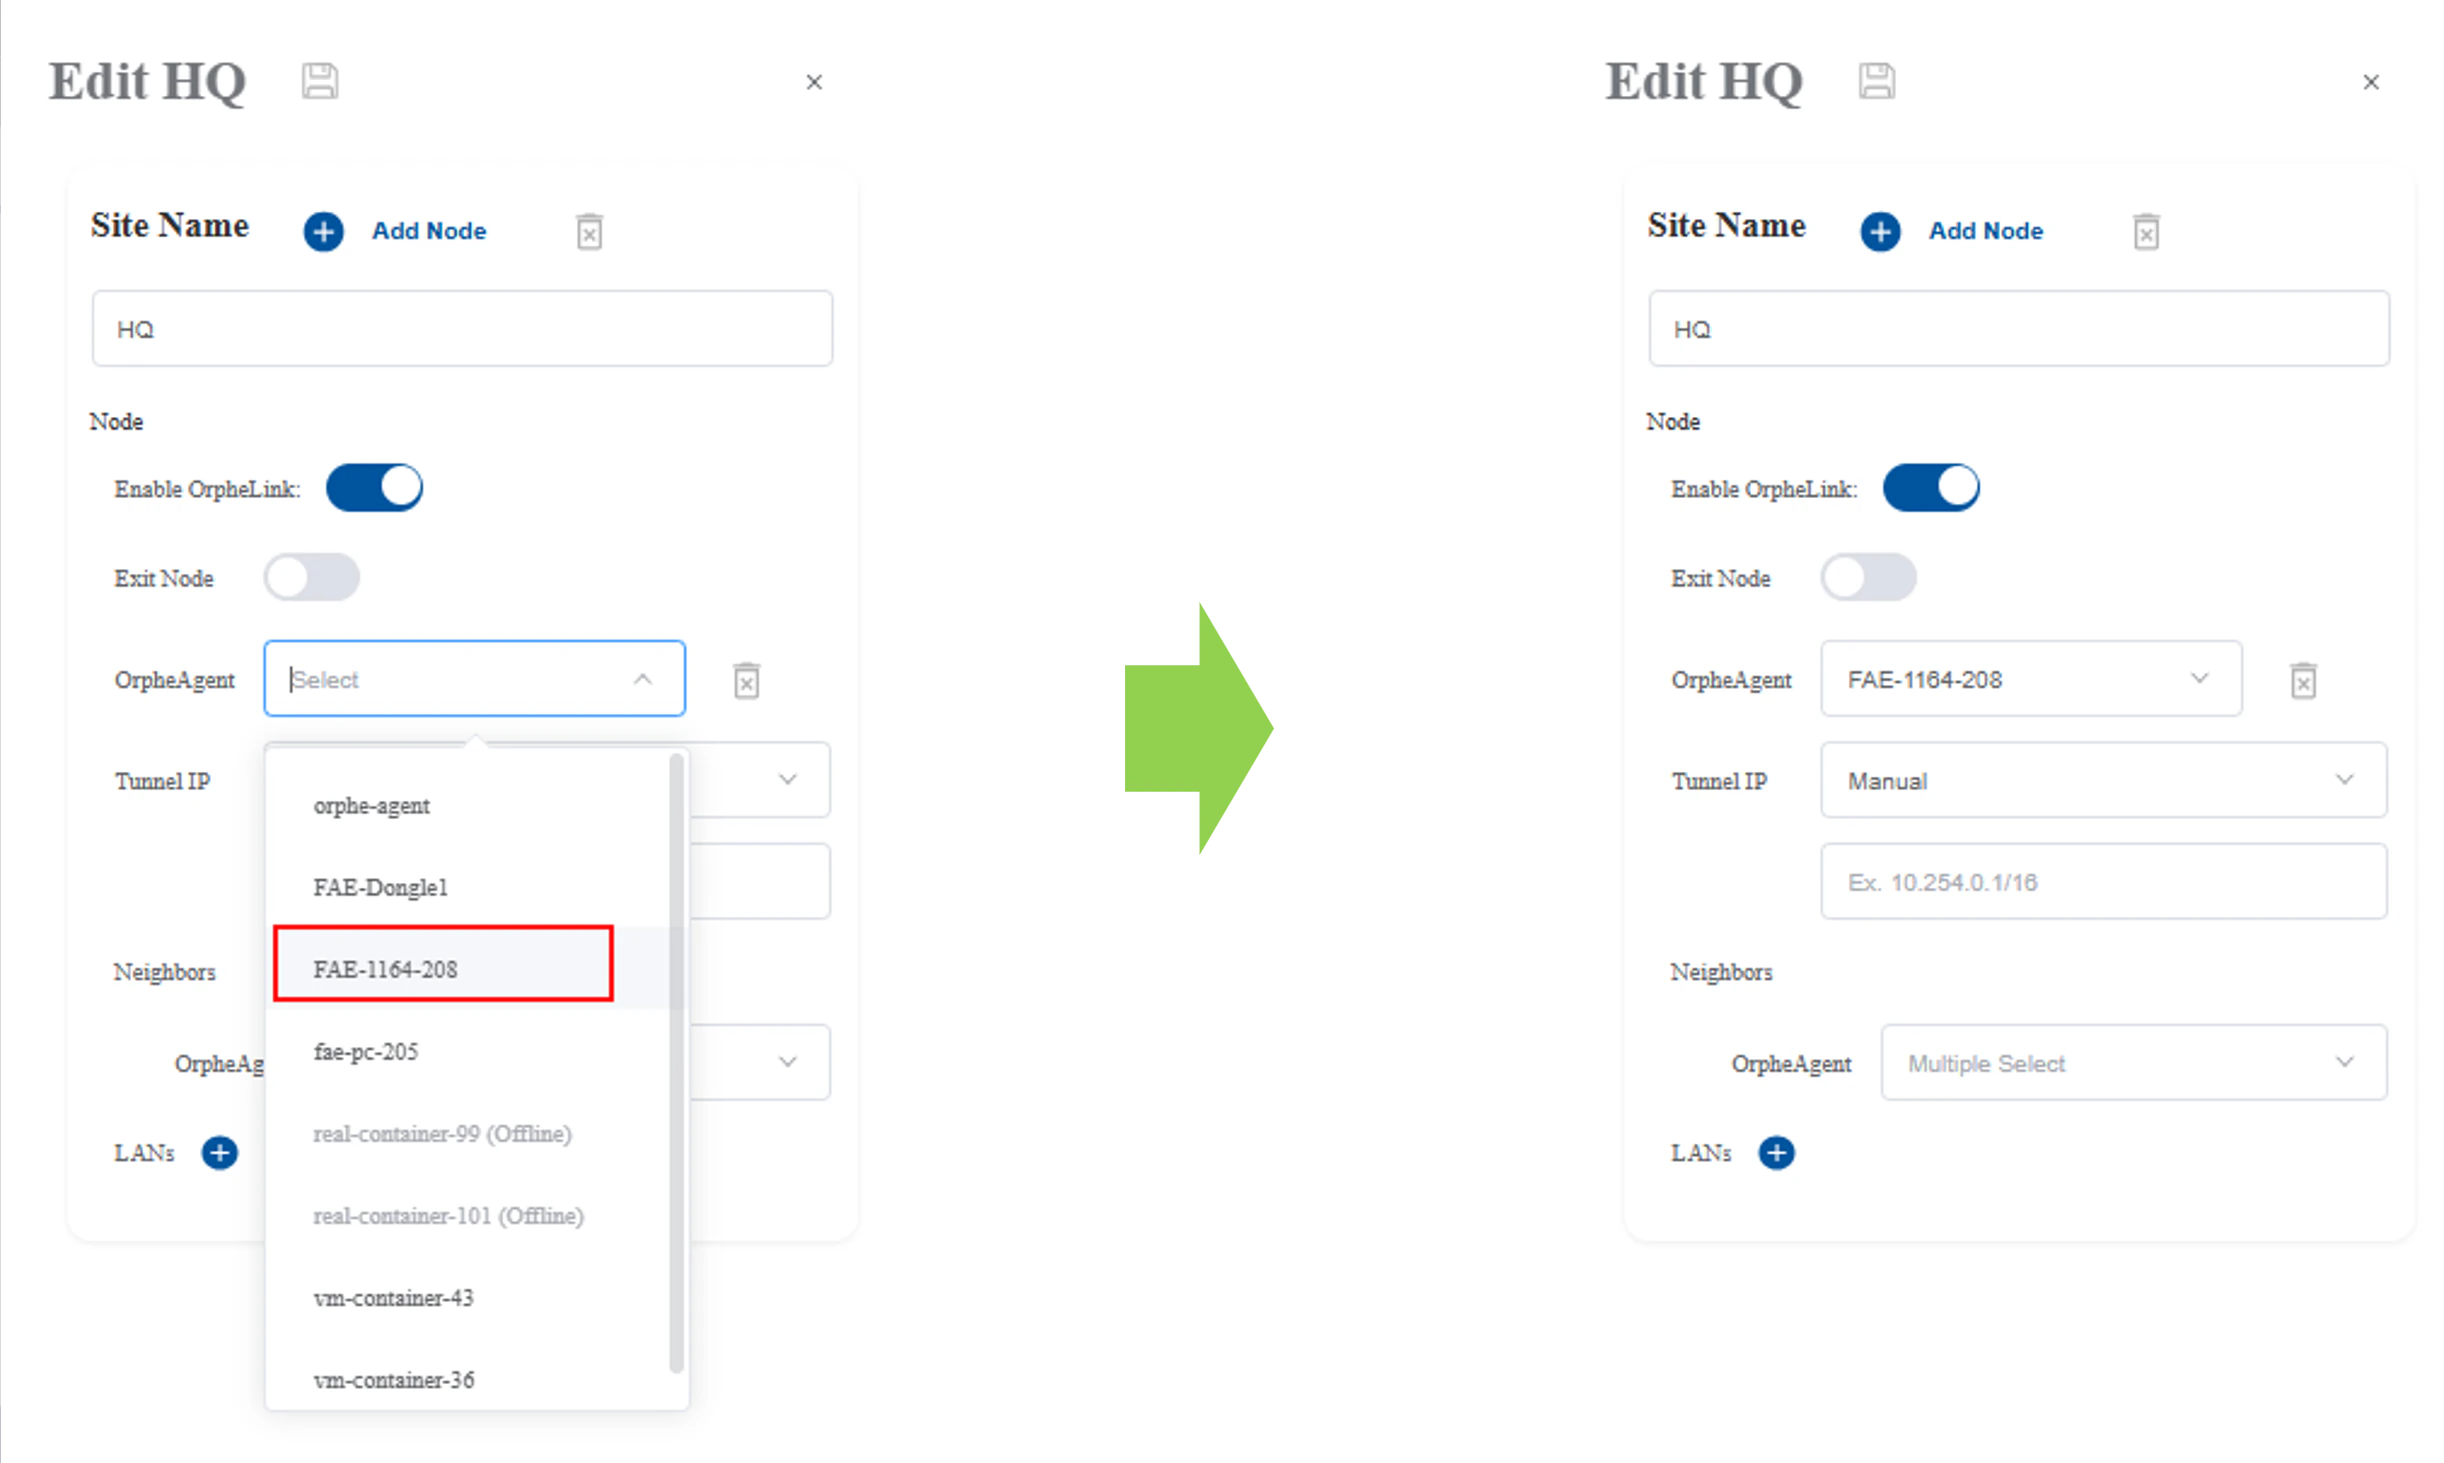
- Set the Tunnel IP to
Autoand select a tunnel subnet.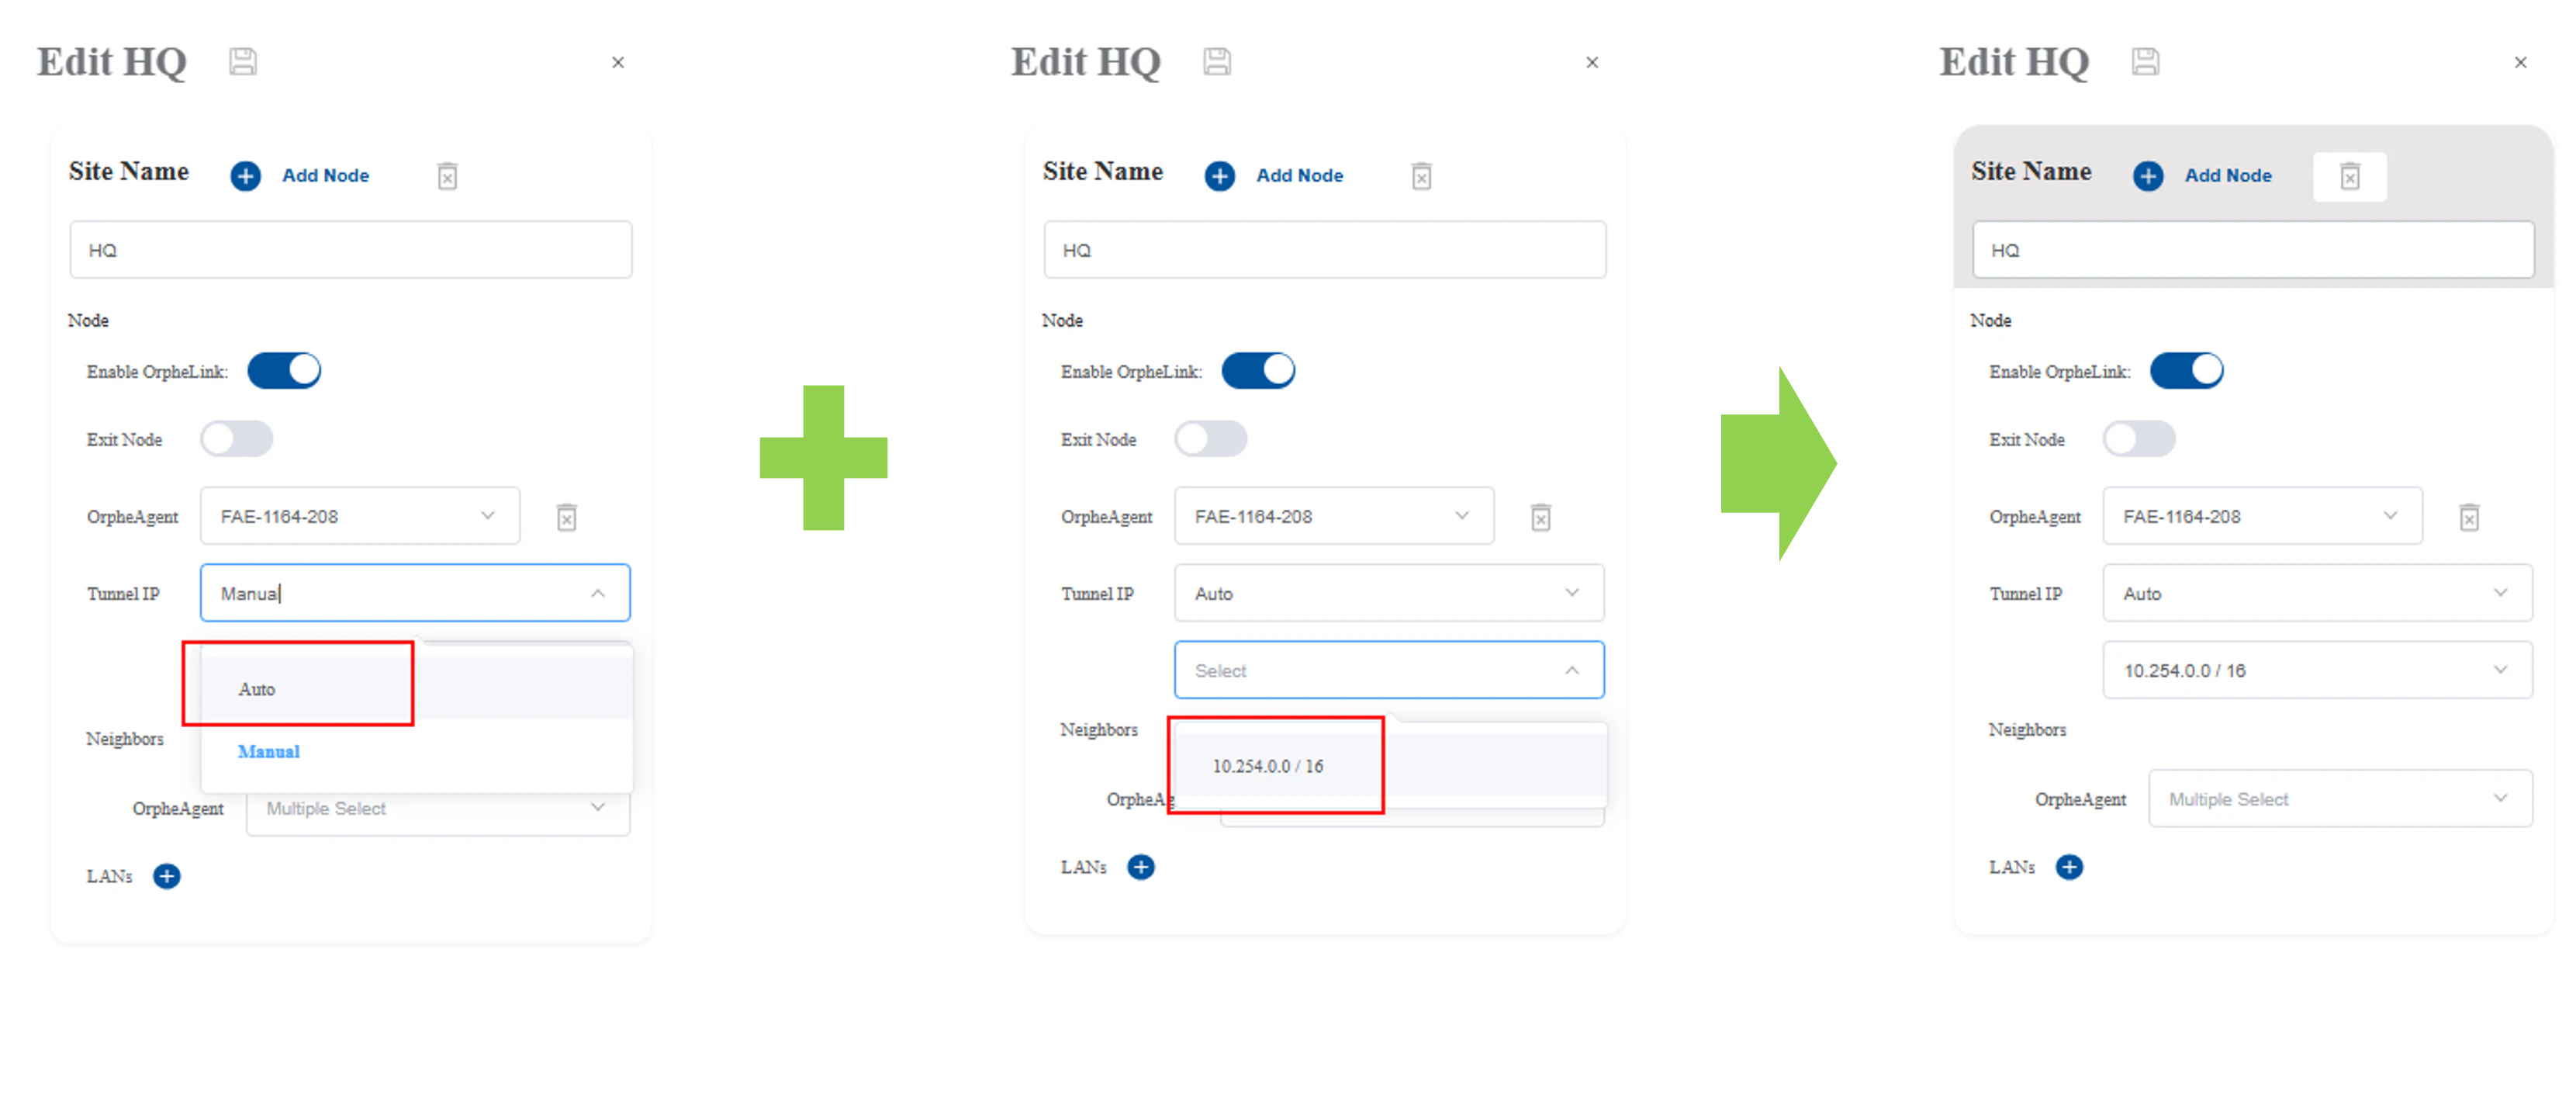
- Click Add neighbors to choose which OrpheAgent nodes to connect to.
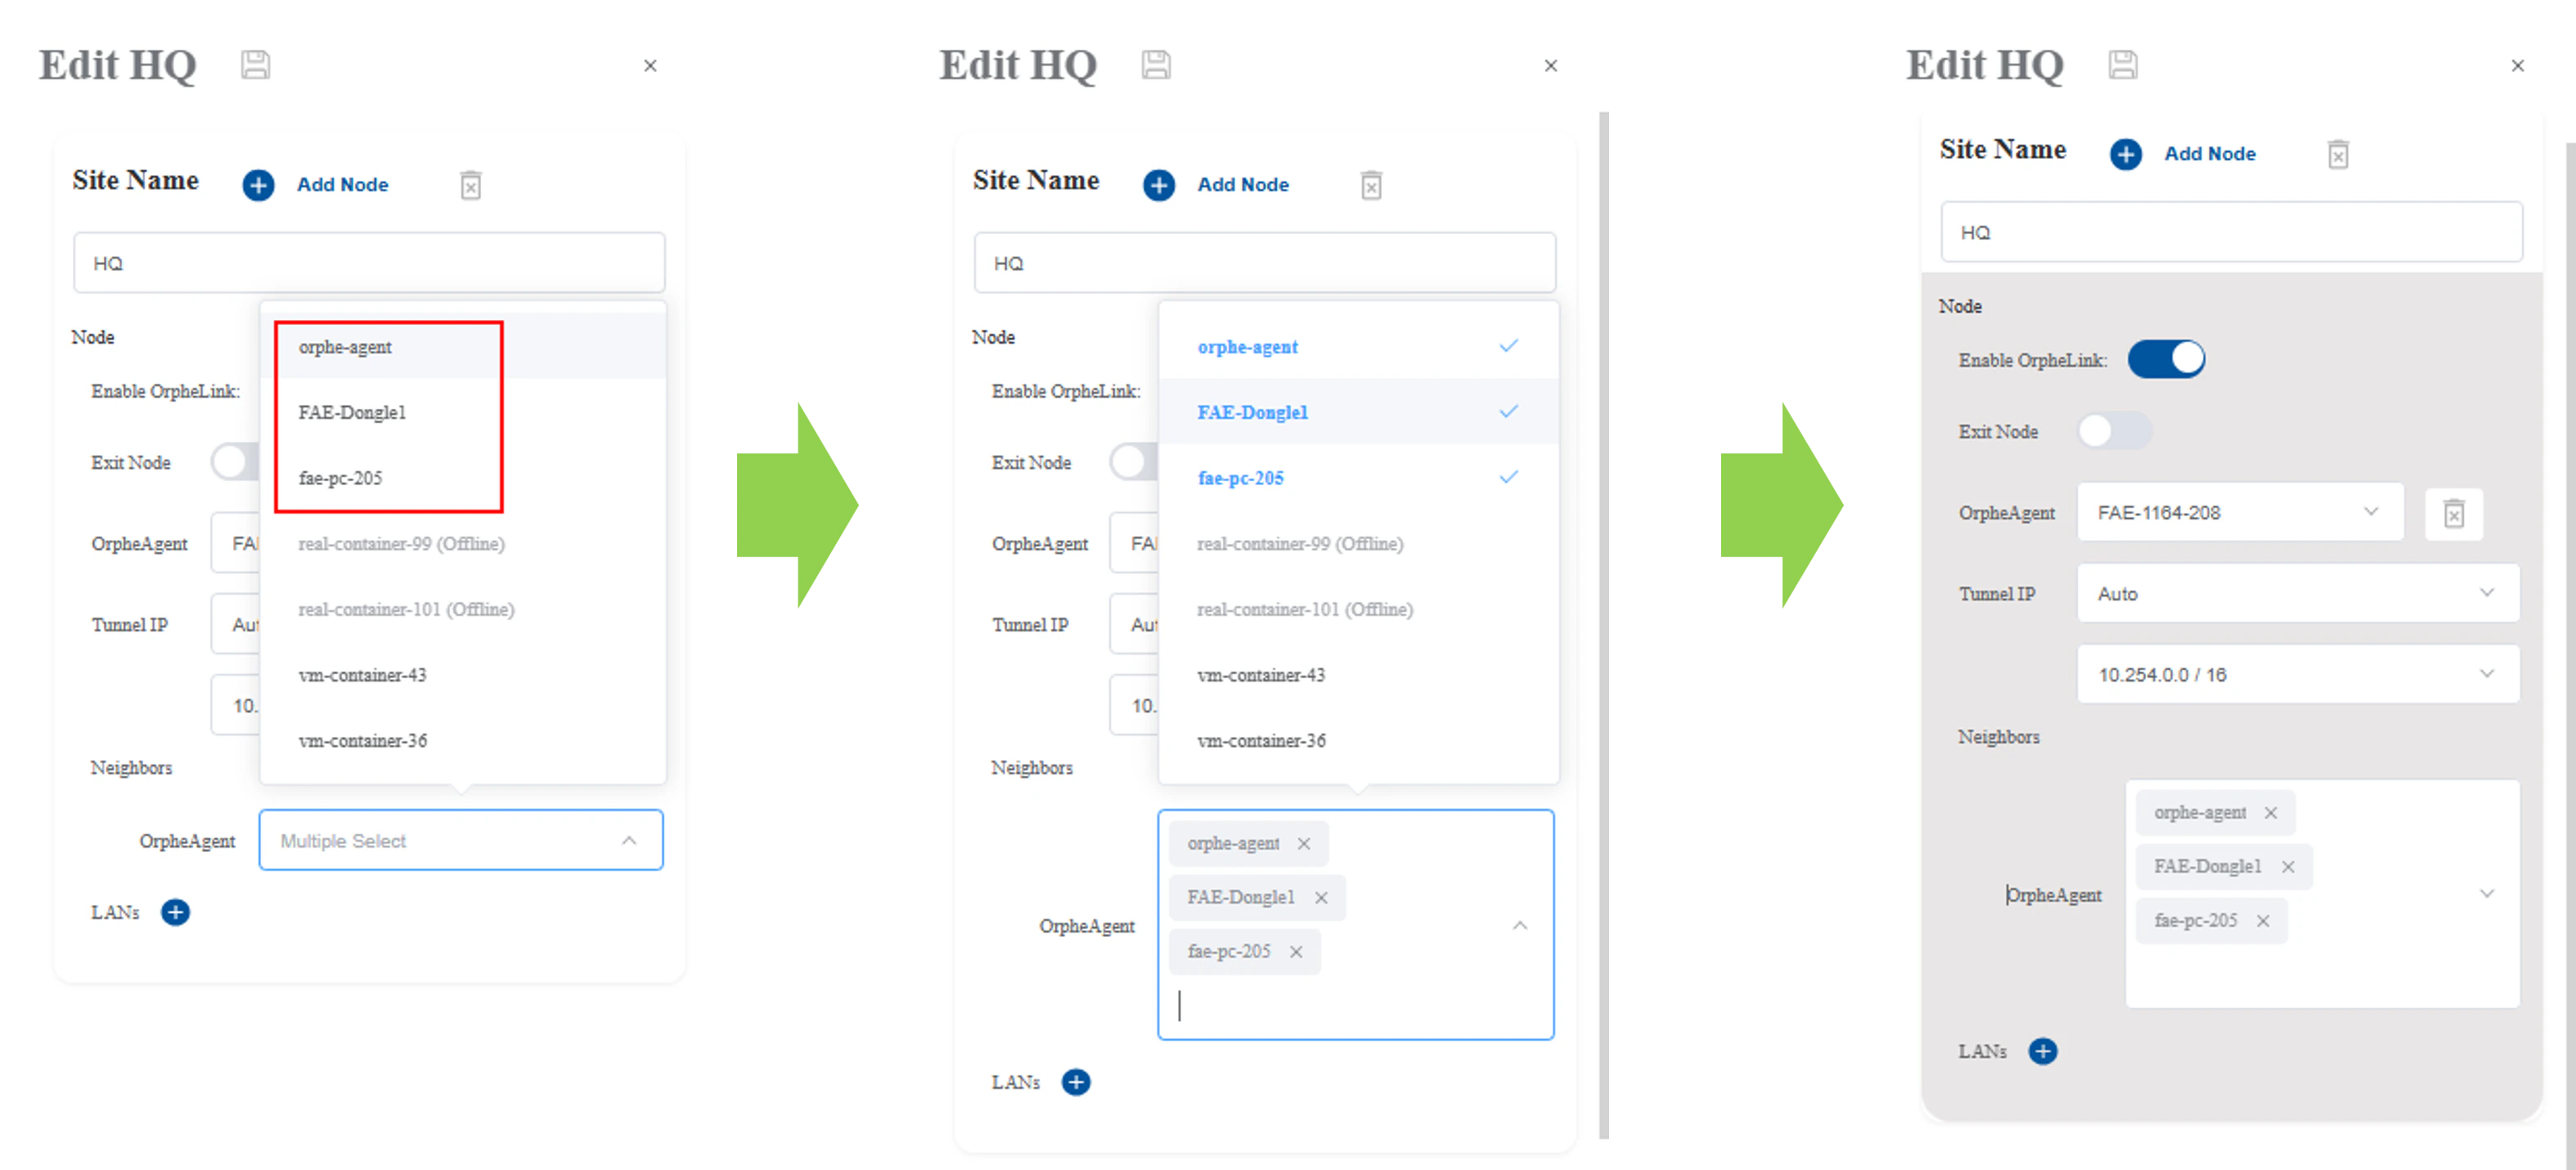
- Click Add LANs and select the appropriate networks from the dropdown list. This configures a LAN-to-LAN connection, allowing endpoint devices to access remote OrpheAgent devices.
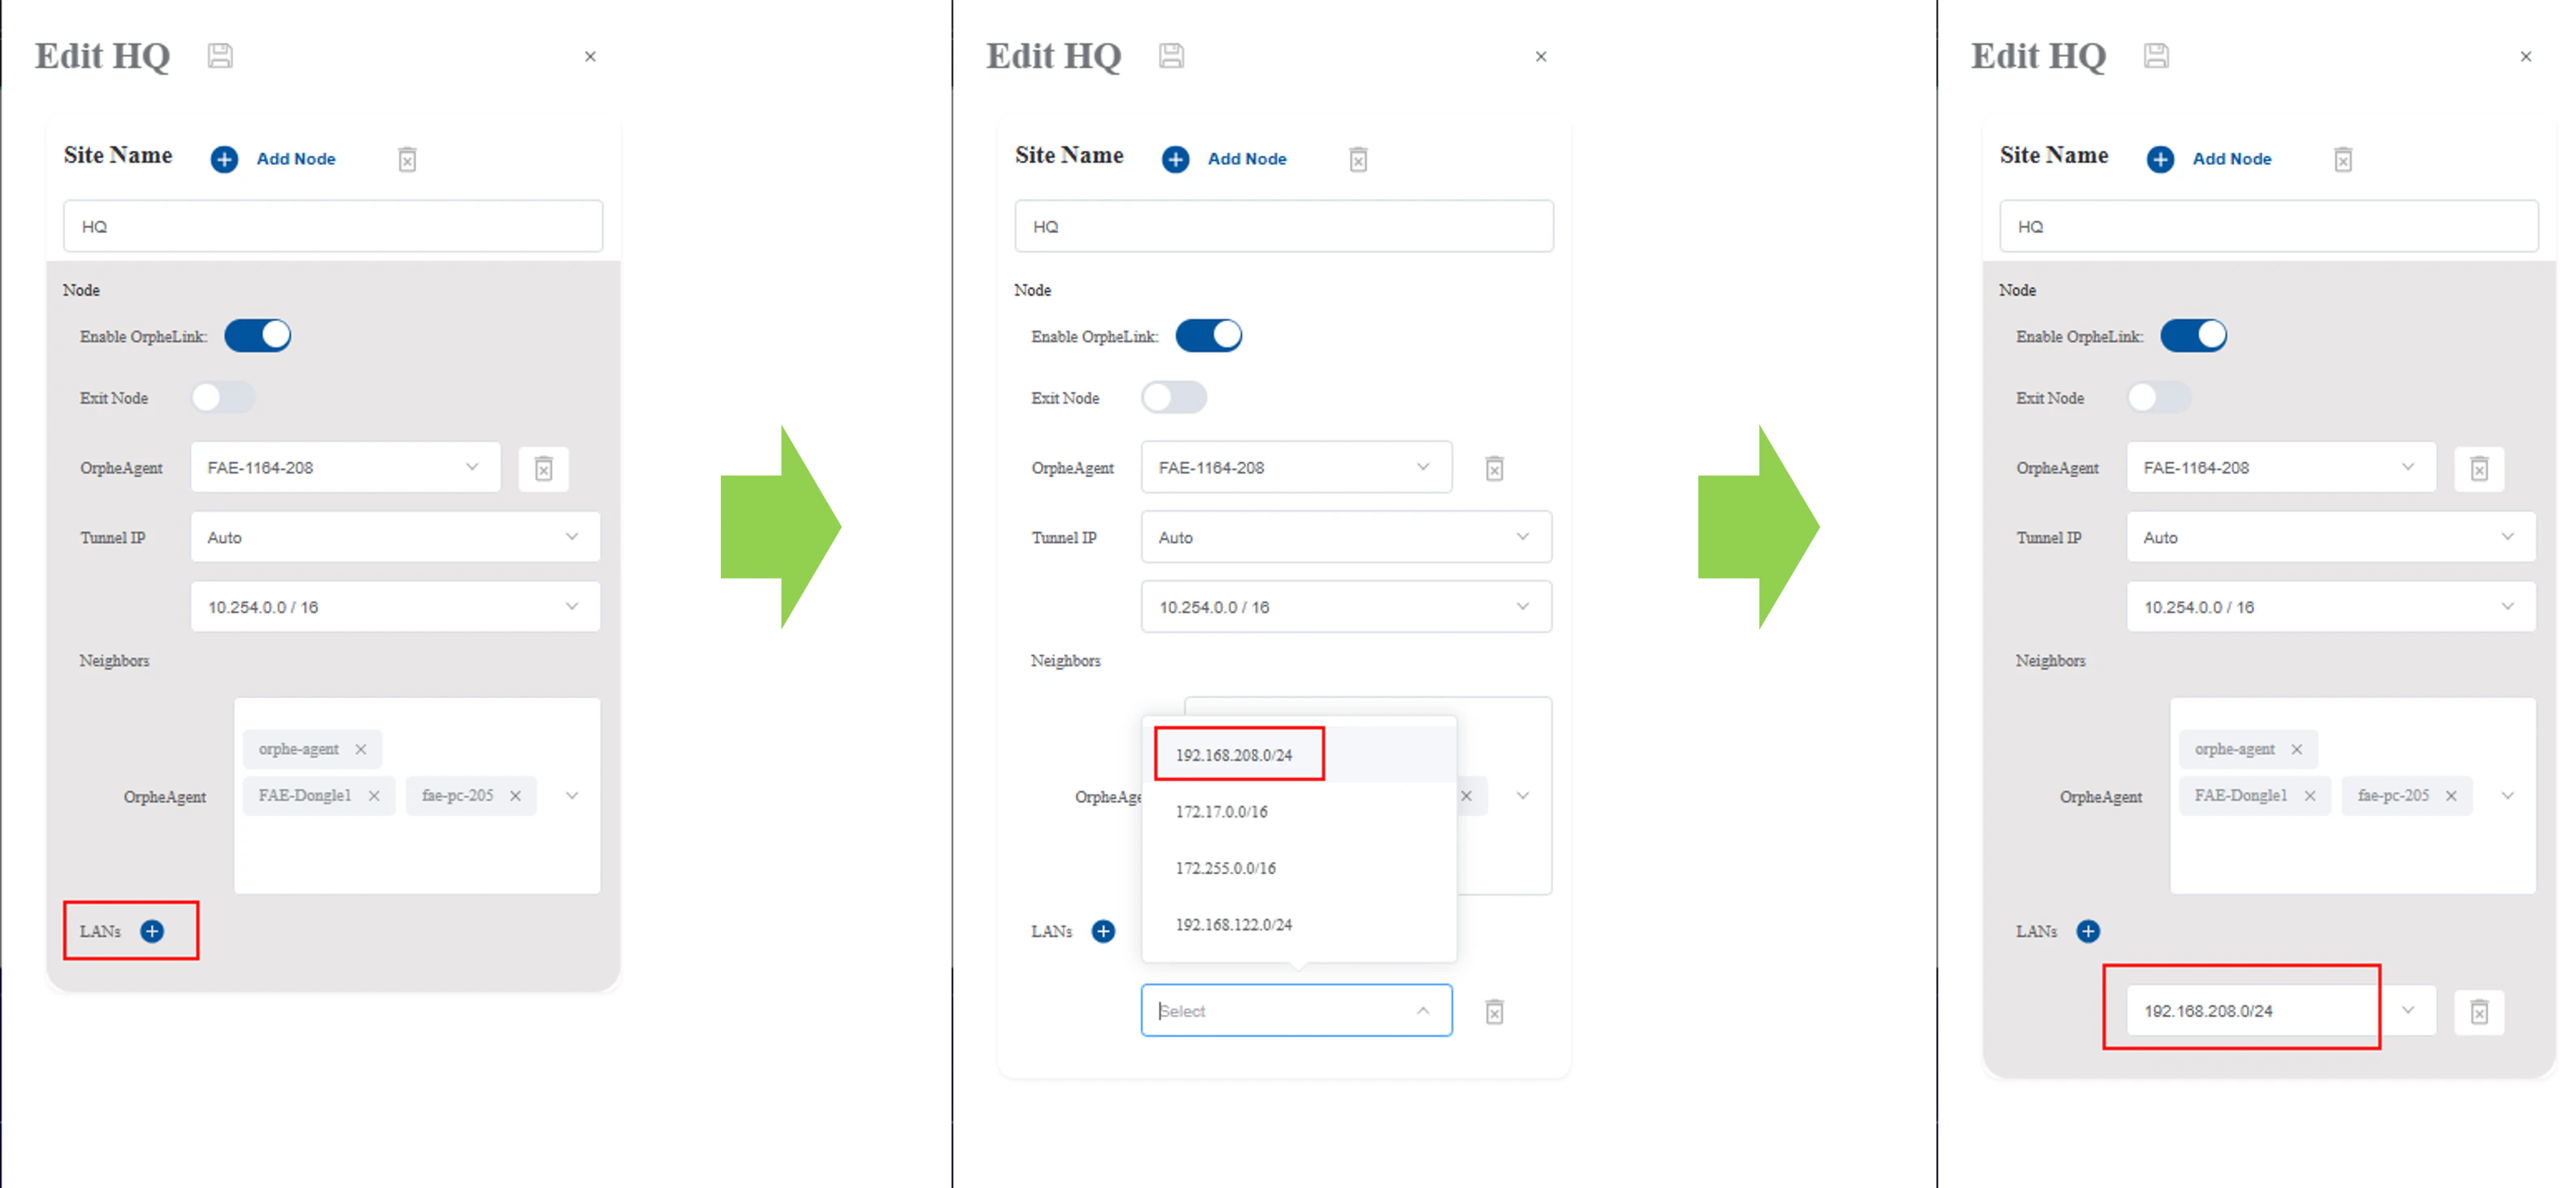
- Click the Save icon.
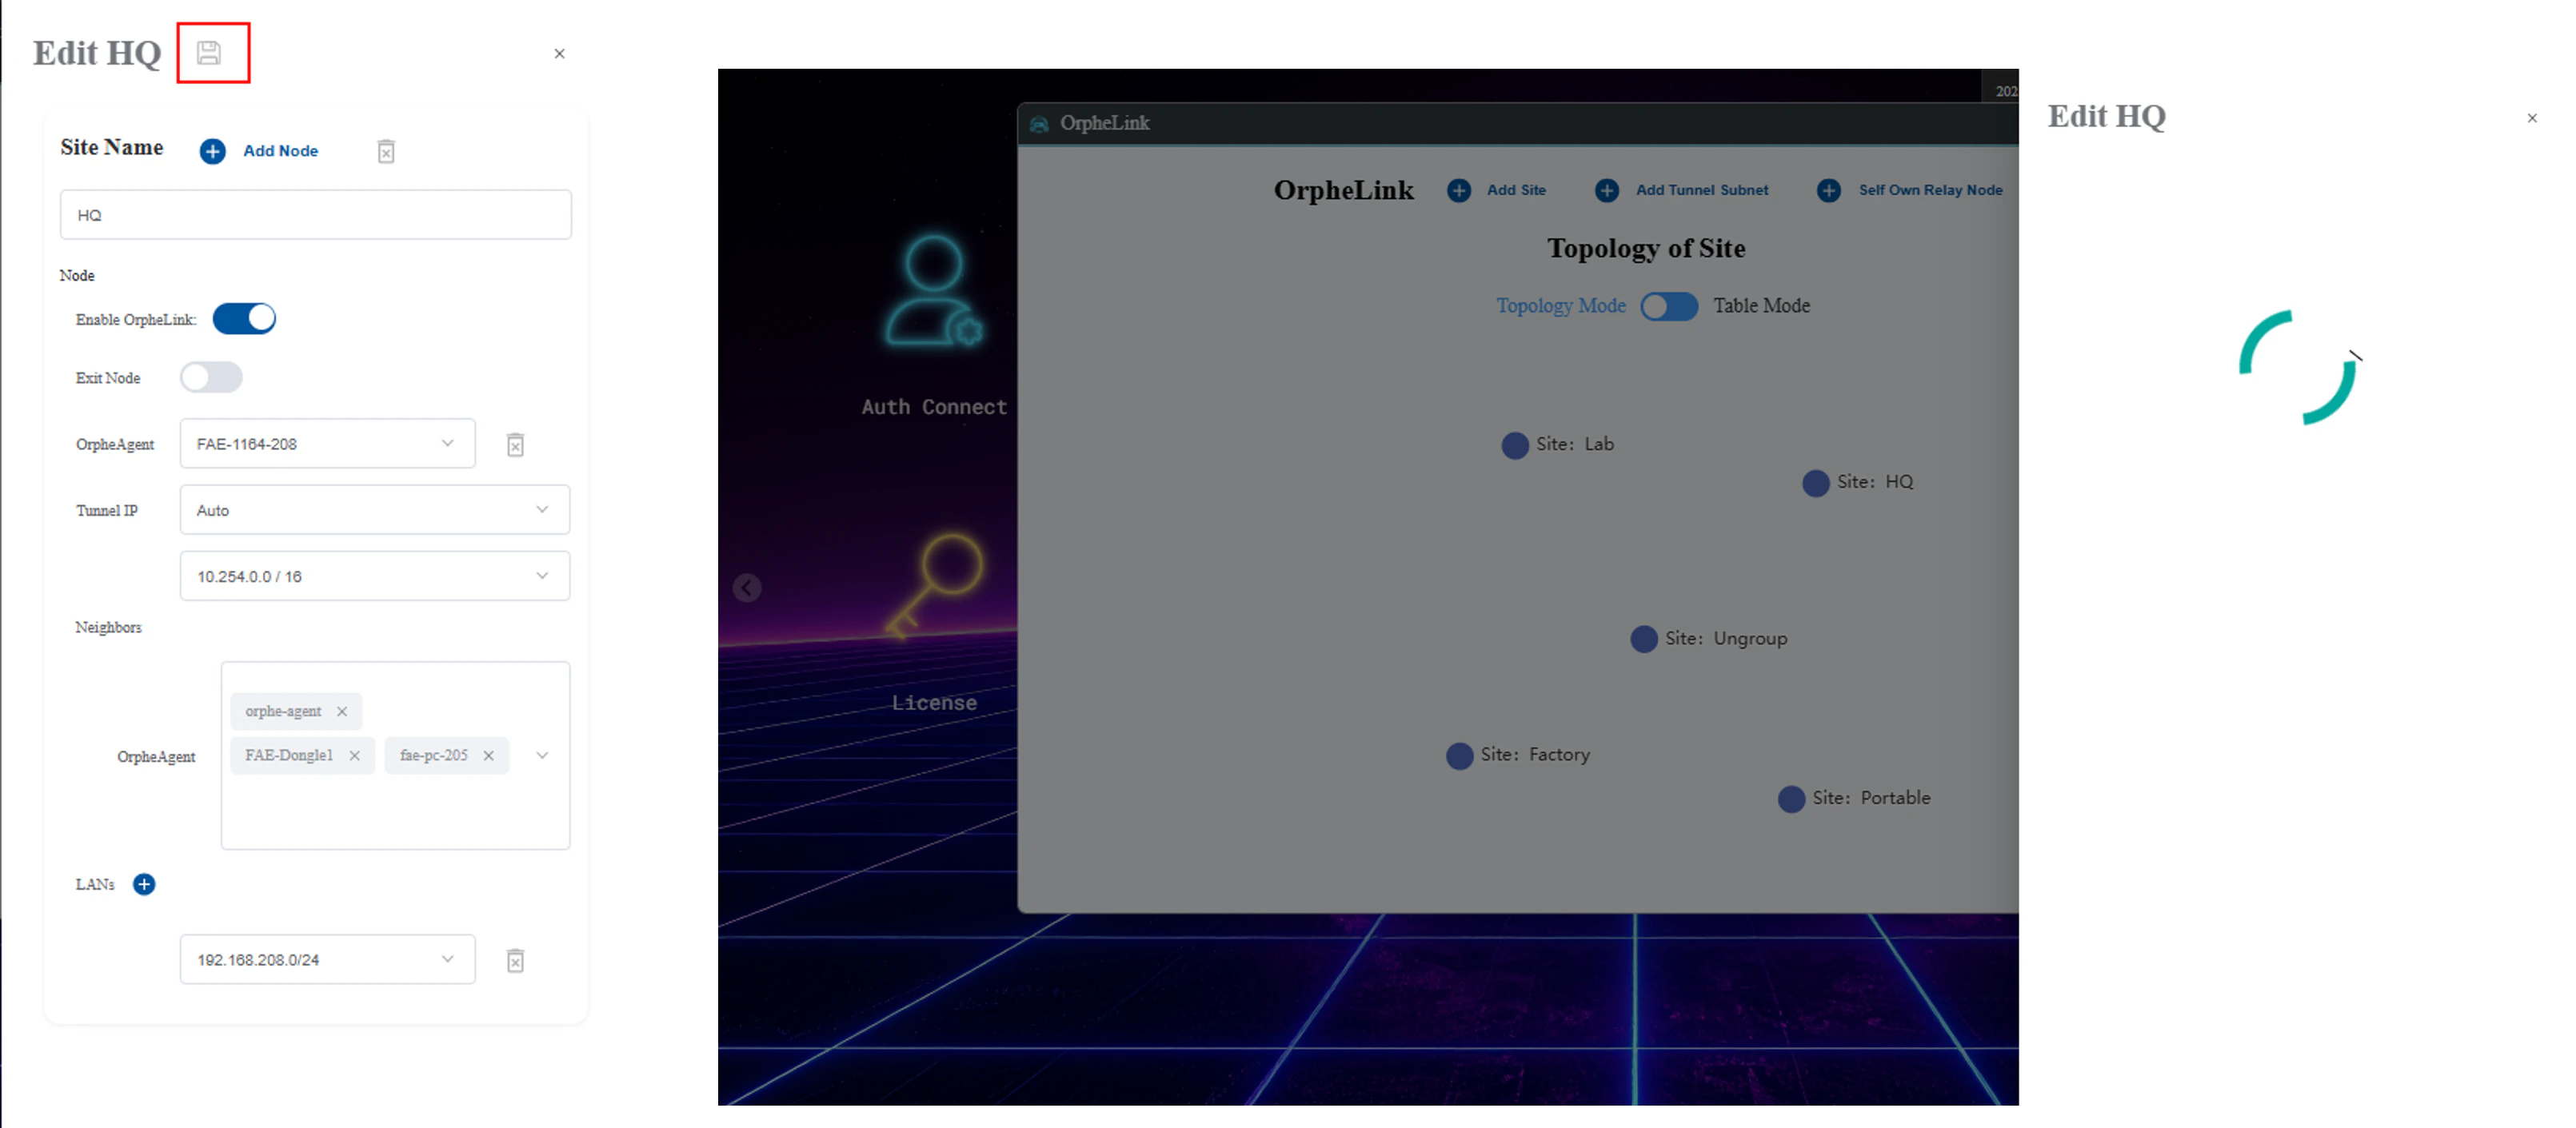
The connection between theHQsite and theUngroupsite occurs because nodeFAE-1164-208is assigned toHQ, while its neighbors (FAE-Dongle1,KSH-4010, andFAE-PC-205) remain in theUngroupsite.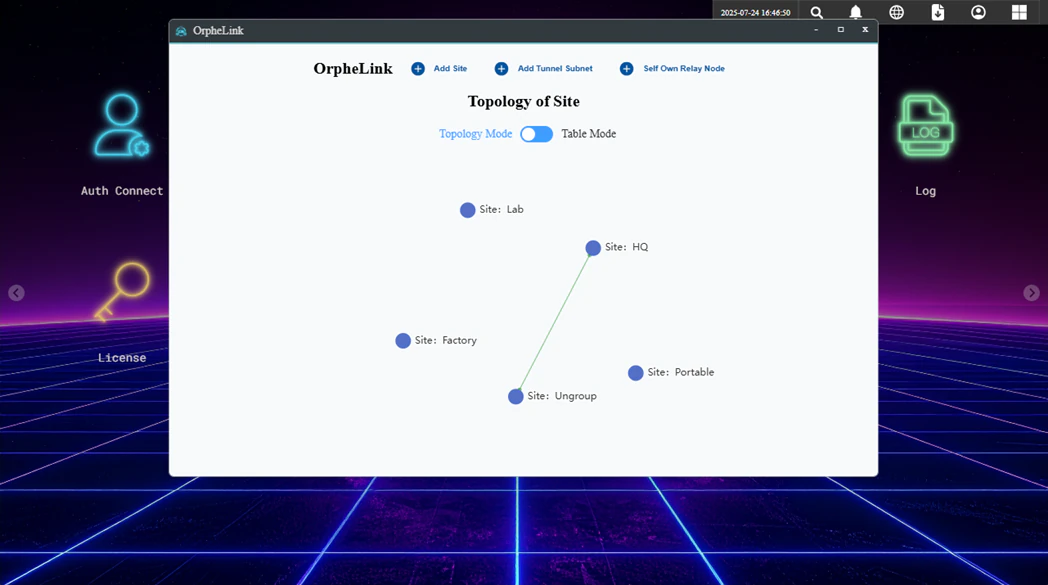
- Configure the remaining sites and nodes using the same procedure:
- Lab: Add node
KSH-4010. Add neighbor nodes and configure LAN connections. - Factory: Add node
FAE-PC-205. Add neighbor nodes. - Portable: Add node
FAE-Dongle1. Add neighbor nodes and configure LAN connections.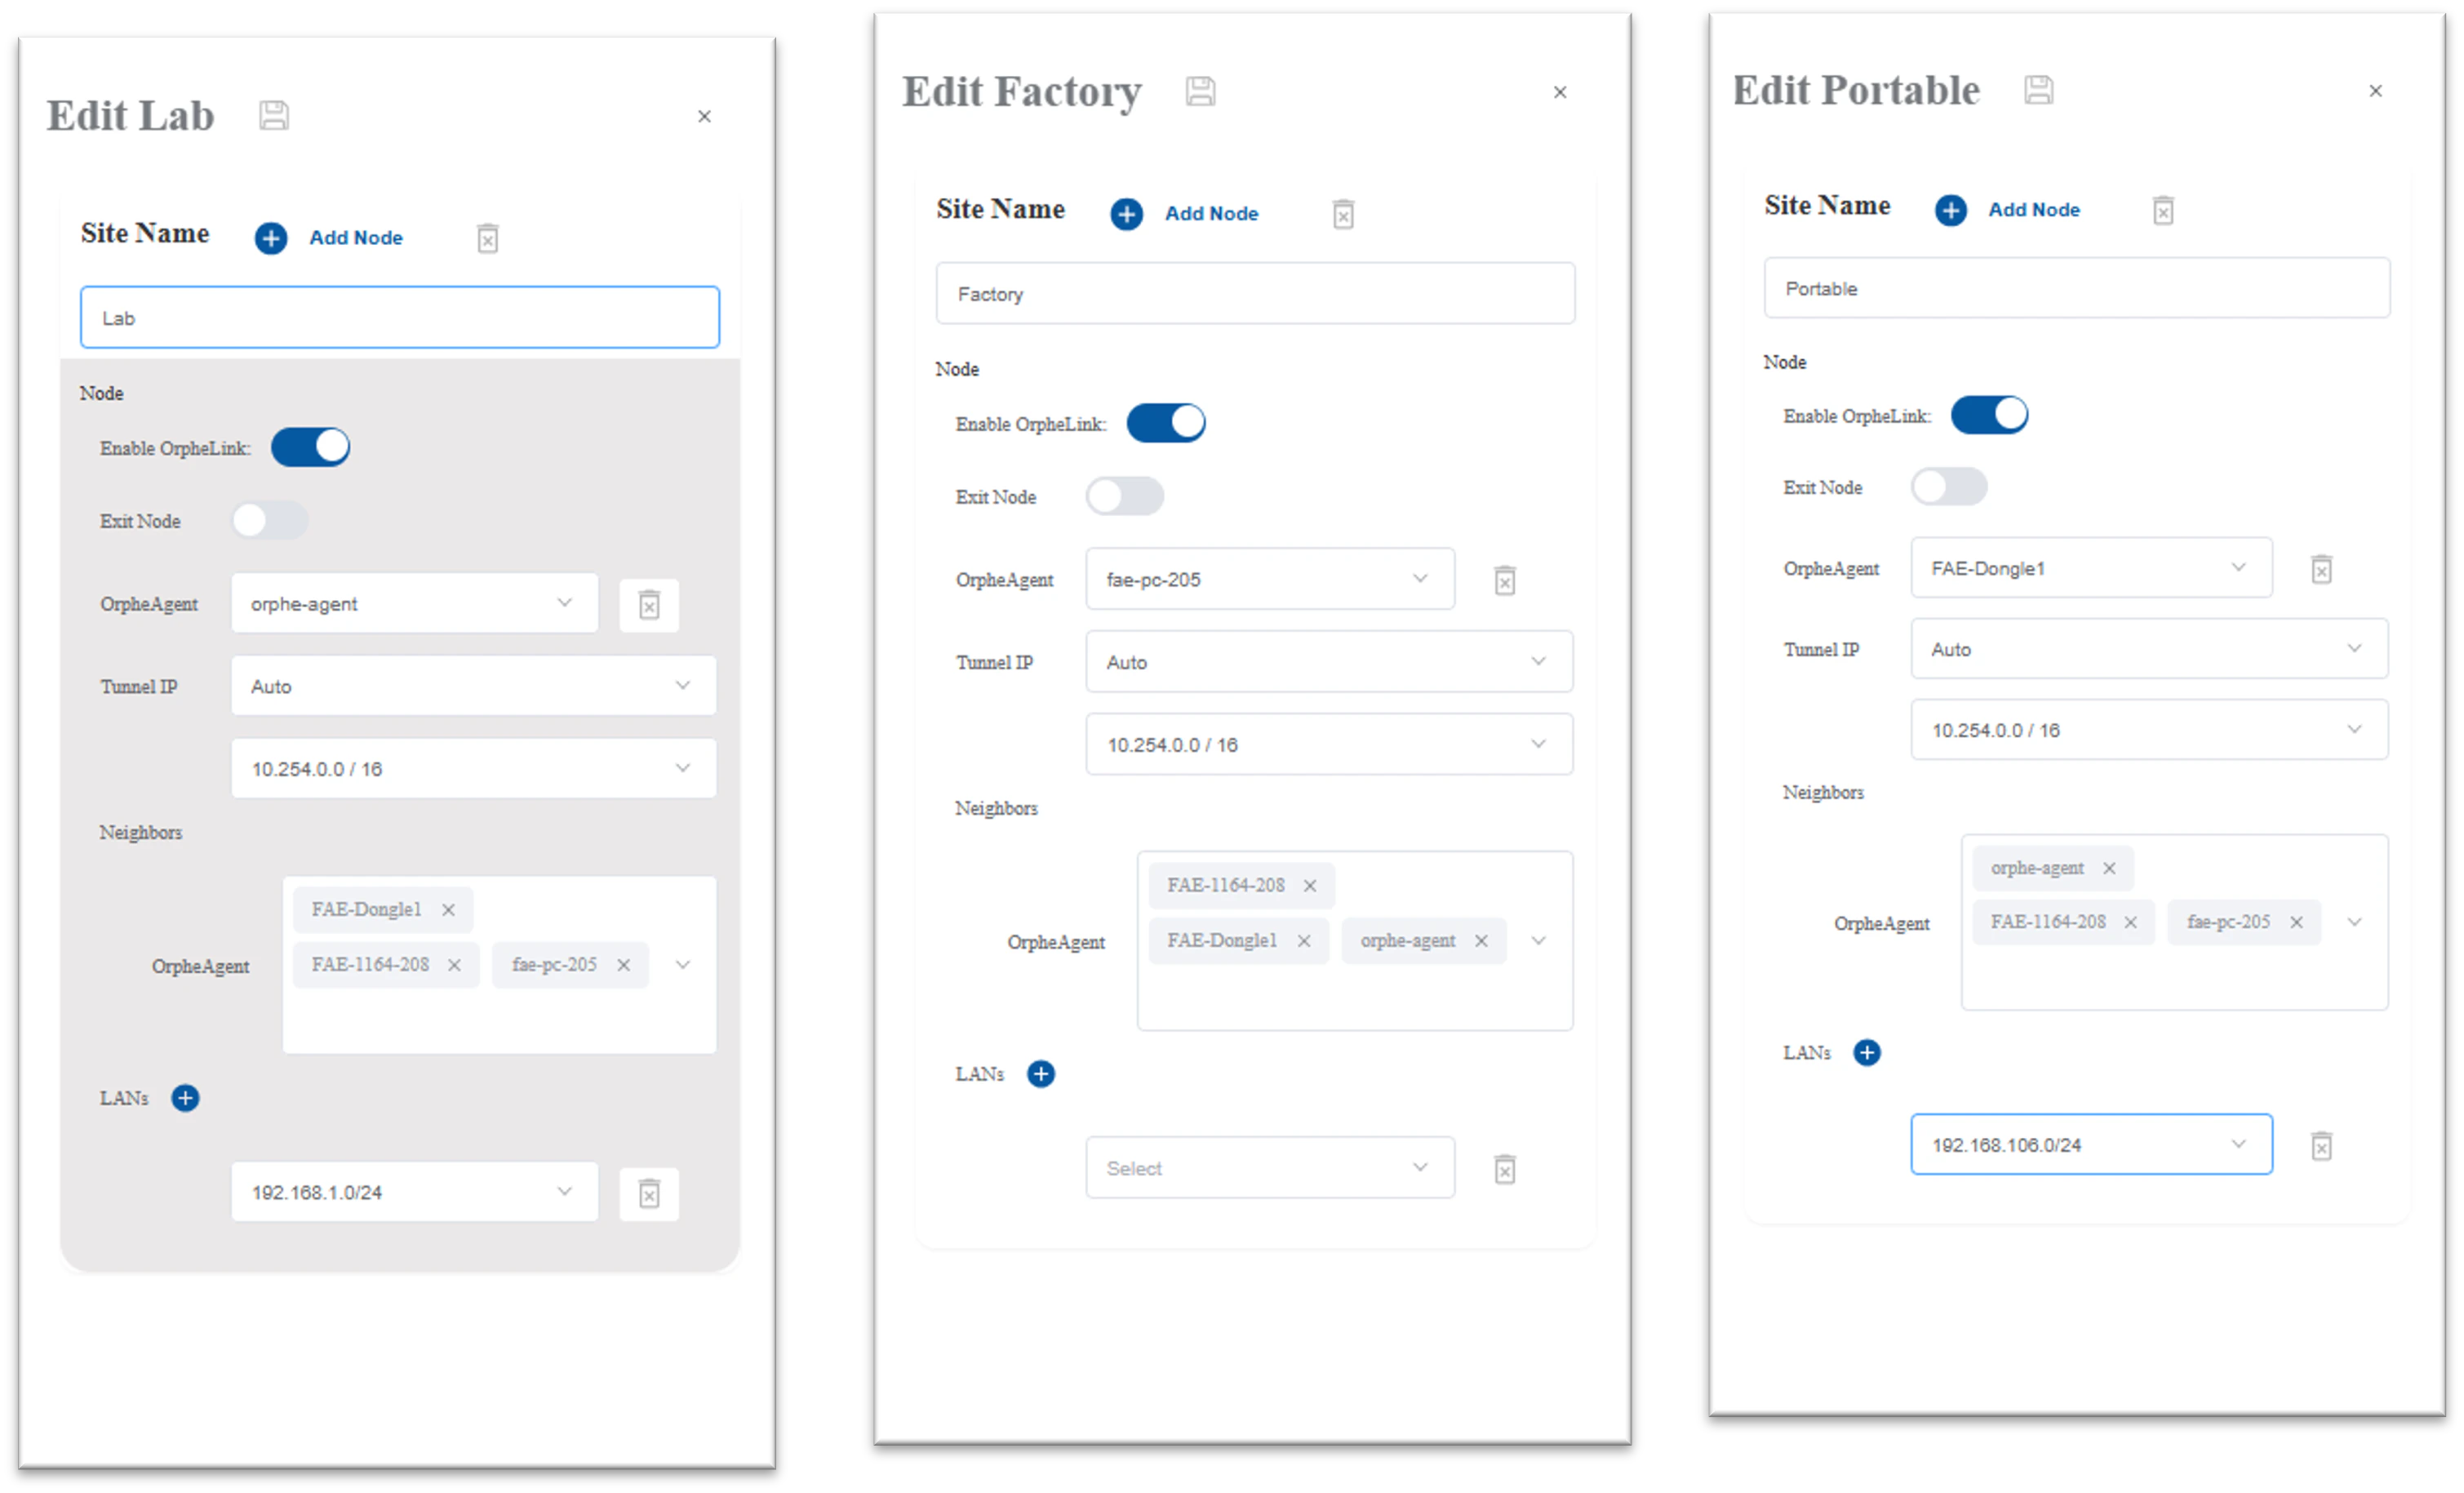
- Lab: Add node
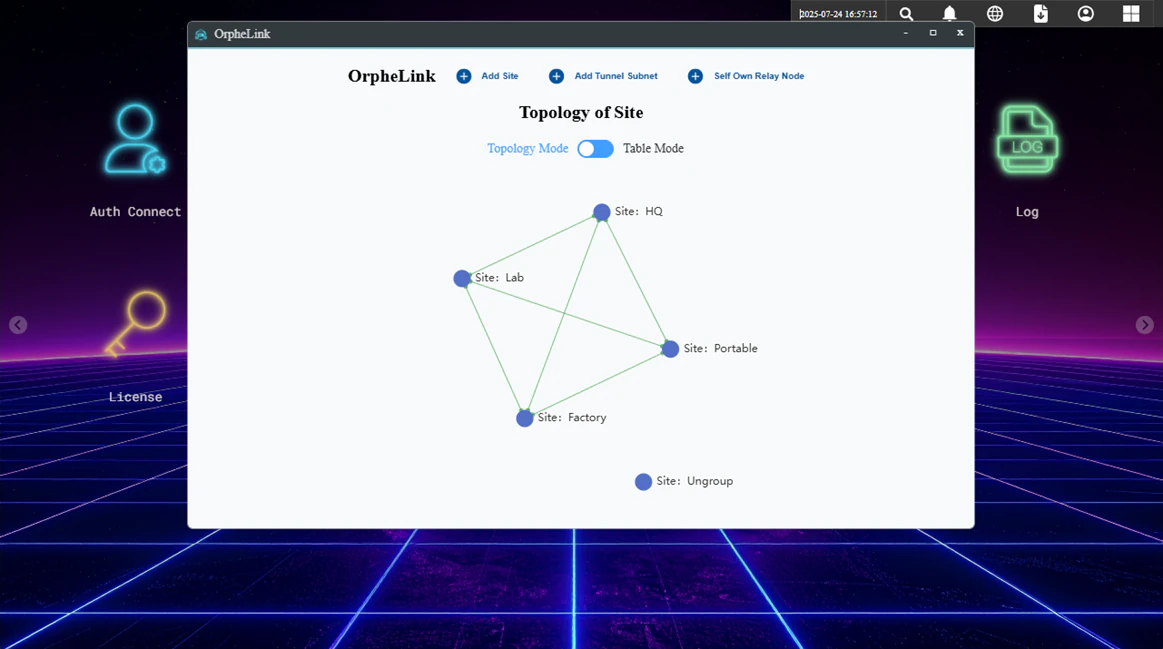
After completing the setup, the resulting site topology is displayed as follows:
Final Configuration Summary
The Tunnel IP and LAN settings for each configured site are listed below:
| Site | Node | Tunnel IP | LANs |
|---|---|---|---|
| HQ | FAE-1164-208 | 10.254.0.4 | 192.168.208.0/24 |
| Lab | KSH-4010 | 10.254.0.2 | 192.168.1.0/24 |
| Factory | FAE-PC-205 | 10.254.0.3 | N/A |
| Portable | FAE-Dongle1 | 10.254.0.1 | 192.168.106.0/24 |
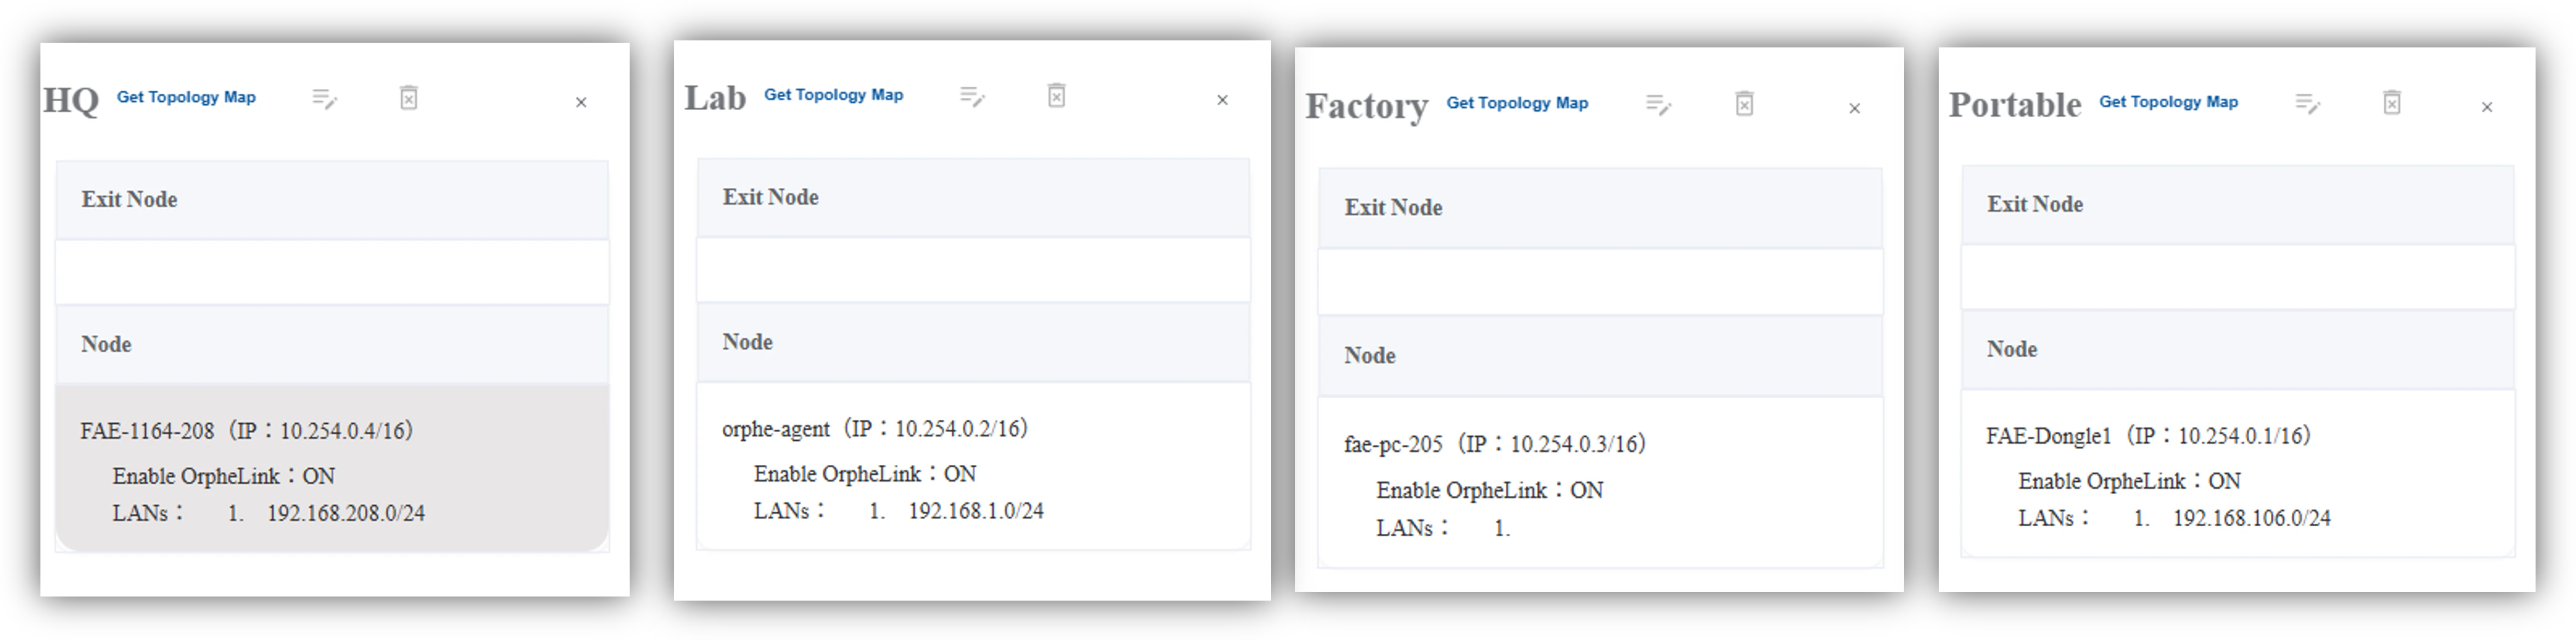
Once this setup is completed, the devices are fully connected and ready to communicate.